

Incident list
The incident list has two entry points. The list inside a channel shows only that channel’s incidents. The list under Incident Management spans channels and can show every incident in the account.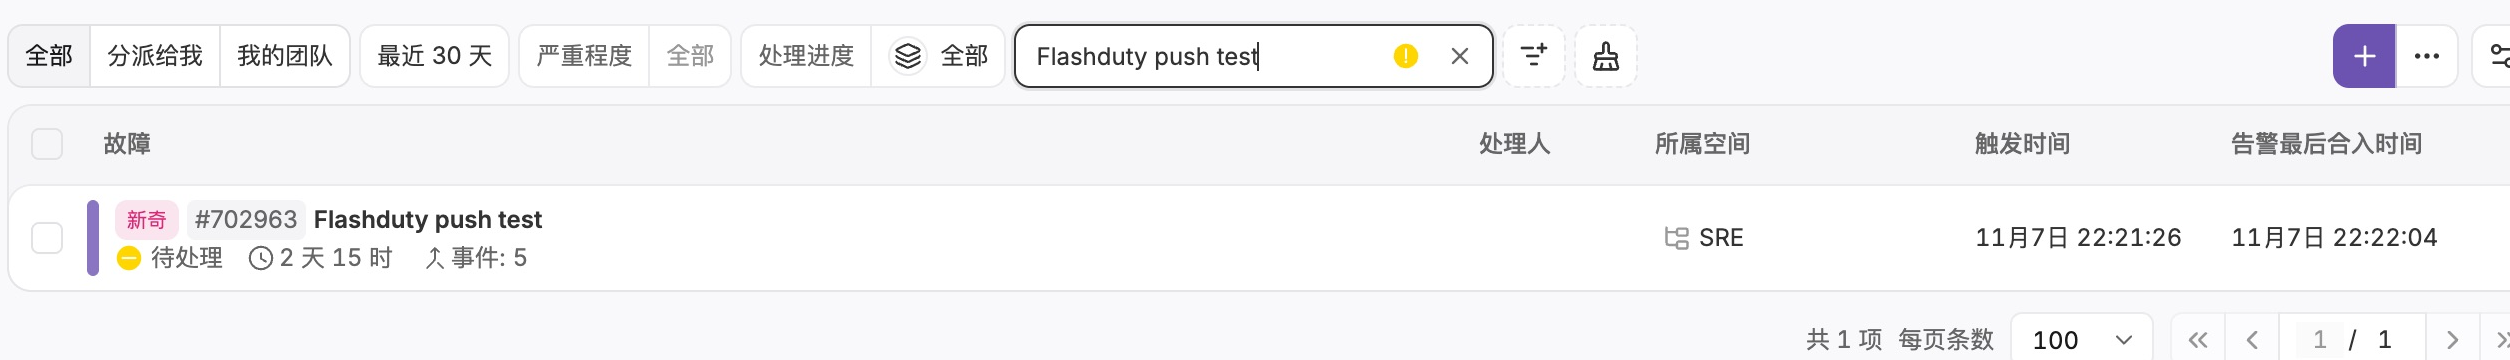
To improve performance, when search conditions match more than 1000 incidents, the system only displays 1000+, not the exact number. Therefore, you can only view 1000 incidents through pagination. To see more, adjust your search time range or use the Incident Query API to get all data.
Using aggregate view
Aggregate view groups incidents in real time by the dimensions you define (a live Group By), for example by severity. After switching to aggregate view, a Grouping Rule selector appears at the top of the list:- Pick an existing rule: Click the dropdown to switch between all saved grouping rules under the current account. Each rule defines a set of Group By attributes (for example, by Severity + Channel +
labels.service) - Create a rule: At the bottom of the dropdown, click New. Select attributes, labels, and custom fields, then name and save the rule for reuse
- Edit or delete a rule: Hover over an existing rule to edit or delete it with the inline icons
- Share a view: The selected rule is recorded in the list link, so copying the link shares the same perspective with other members
To improve performance, in aggregate view, the system matches at most 100 records for aggregation. Therefore, the list you see may not contain all matching data. If this concerns you, switch to list view.
Using more filters
More Filters lets you combine many dimensions. Common uses:- Search for incidents triggered by the “Host Down” alert policy based on
checklabel - Search for incidents marked as “false positive” based on the false alarm field
- Set Unfinished actions / follow-ups to Yes to surface incidents that still have open work to wrap up
- A label value must equal the value stored on the incident, case included. A value containing
*or wrapped in/…/is compared literally: the system doesn’t expand it into a wildcard or a regex, tells you “Label values match exactly; * and /…/ are not supported. Use the search box for a partial match”, and leaves that condition out of the query - Custom fields list single-select, multi-select, and checkbox fields only, and their values also match exactly. Text fields can’t be filtered by field; use Search instead. Unsupported fields show “Only single-select, multi-select and checkbox fields can be filtered. Use the search box for text fields”. Saved filters are cleaned by the same rules when restored
- One label or custom field can hold several values at once: the values chosen under the same item match any of them (a multi-select field matches by containment), while different labels and different fields still must all match. A checkbox field only has
true/false, so choosing both says nothing extra and only the first applies - For a partial match, use Search at the end of the filter bar. Wildcard and regex syntax applies only inside Filter Conditions, which configure rules such as escalation, silence, and inhibit rules
Row content
Beyond the title and progress, each incident row surfaces two key counters:- Associated alerts: total number of alerts grouped into this incident
- Alert events: cumulative count of events merged into the incident. When a new event has been merged in the past 5 minutes, the merge icon turns orange to signal that the incident is still actively aggregating
Batch operations
After selecting one or more incidents in the list, use the action bar above the list to perform batch operations:
Except for AI Analysis, the above batch operations require incident update permission.
Custom rendering
Click the Settings button in the upper right corner of the incident list to customize display content and interaction behavior:Incident details
Incident details is the main entry point for investigating an incident and shows everything known about it; the default Incident Overview tab gathers what you need most often.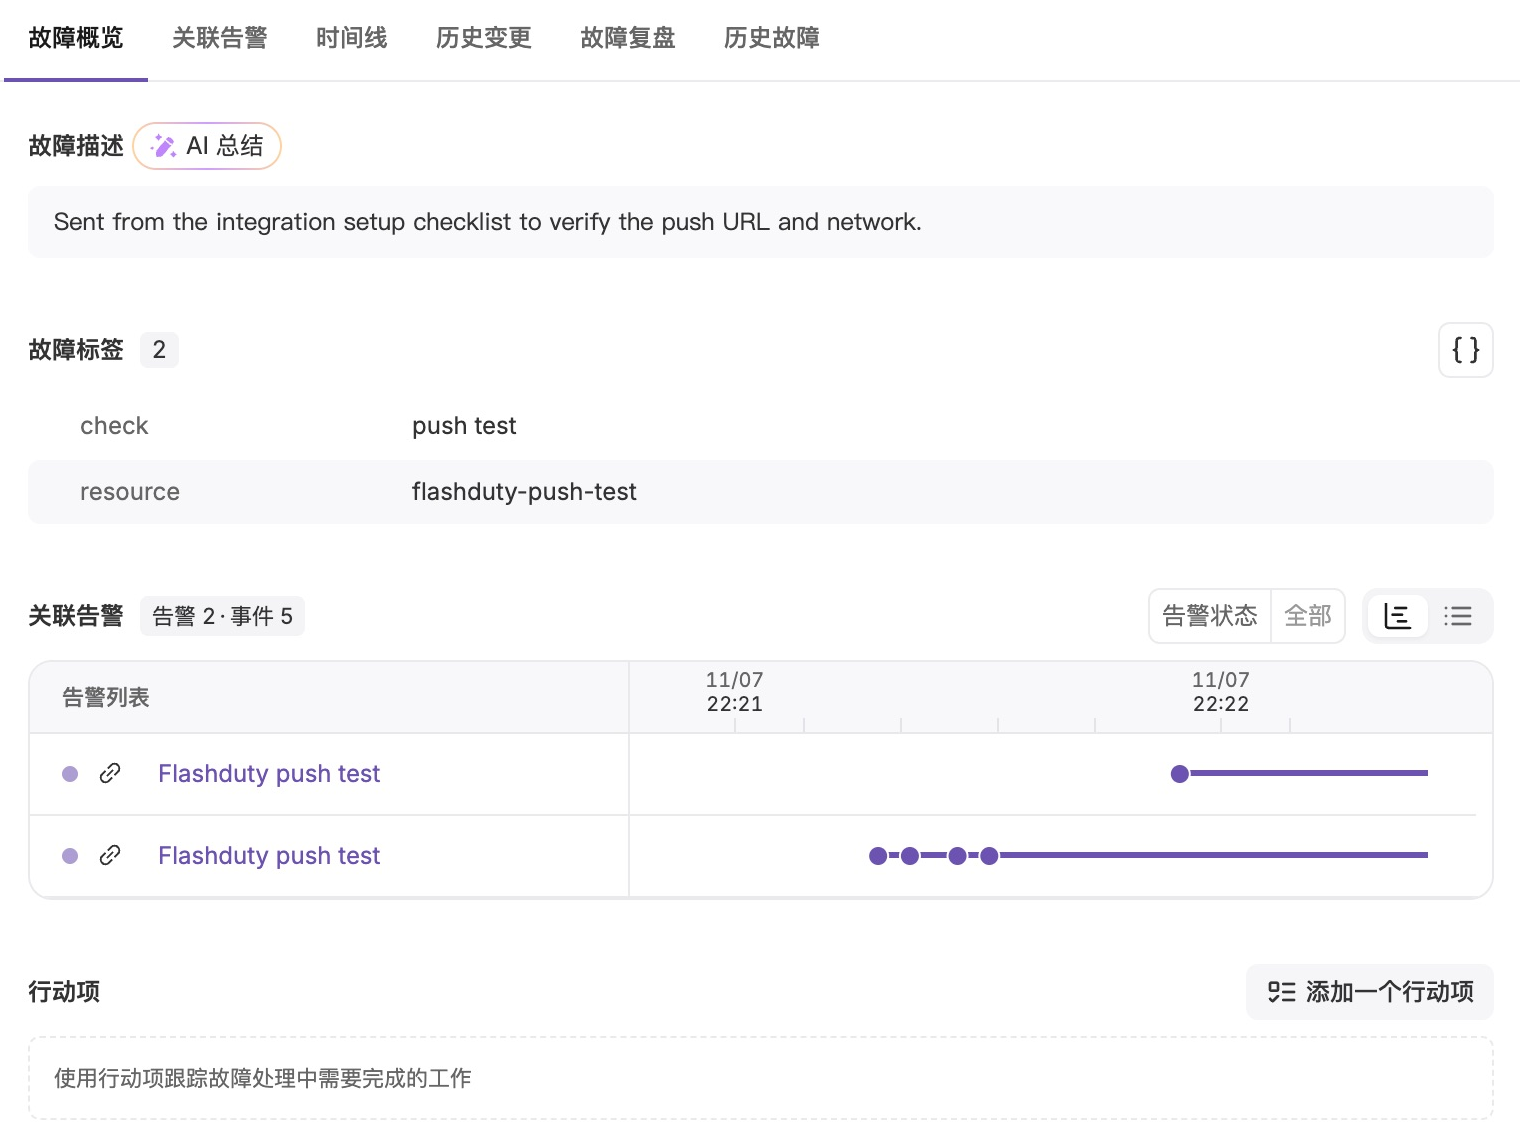
Label display
Incident labels appear in the Details area of the details page. For how values are rendered (links, RUM issues, images, ARNs, times, query expressions), see What is an incident · Label value rendering. To get back to the query as it was when the alert fired, open the Query Workbench from any of these places:- The hover card on a system label: hover over query-type system labels such as
__alert_rule_queries,__alert_rule_values, and__alert_rule_relate_queriesto see the query and the values at trigger time - The comprehensive info panel’s investigation entries: the Investigation block in the right-side panel (see Investigation below)
- The “Investigate” popover in the Associated Alerts tab: every alert row builds its entries from that alert’s own labels
AI summary
Click the AI Summary button in the details area to generate a structured summary from the incident’s associated alerts (up to 20):- Summary: A one-sentence description of what happened
- Impacts: Key affected resources such as services, systems, environments, and instances
- Actions: Immediately actionable investigation and remediation steps (up to 3)
Comprehensive info panel
The comprehensive info panel on the right side of the incident details page consolidates auxiliary information around the incident. From top to bottom:Investigation
For incidents aggregated from Monitors alerts, the comprehensive info panel gains an Investigation block between Attributes and Images. It does not show live query results: it renders the investigation-entry snapshot that the alert rule produced at the moment the alert fired. Each entry is one row showing the entry-type icon (query or dashboard), the purpose configured on the rule, and the data source (name plus type icon). When the rule has no purpose, a query entry shows its query expression instead, and a dashboard entry shows the dashboard title and its location path (the whole dashboard, orTab › Panel). Entries that render with a problem carry an orange dot on the type icon.
- Hovering an entry opens a detail card with the full query expression (copyable), the named variables (filled in from the alert’s labels; unresolved ones are highlighted in red), and the time range — the relative window on one line (for example “60 min before → 10 min after the alert”) and the absolute start and end on the next. An Open button at the bottom opens the corresponding view in the Query Workbench or dashboard in a new tab
- The number next to the heading is how many entries the snapshot holds; the N with issues badge counts the entries that render with a problem (query failed to render, dashboard variable unresolved, data source or dashboard deleted or unauthorized)
- Only the first 3 entries show by default; the rest sit behind N more, which expands and collapses
- Below the entries are the Related alert rule card (rule name plus data source, clickable through to the rule) and the rule’s Queries: main queries are listed by
A/Bwith the value at trigger time, hover for the full expression with a copy button, and a no-data alert is marked No data on the matching main query; related queries show the result at trigger time: a result table for statistical queries, and for a VictoriaLogs / Loki related query whose query mode is Raw one log line per row with its fields laid out ask=vand the fields that do not fit collapsed into +N fields; the hover card shows at most 3 rows, and View full data next to its heading opens the query workbench with everything
- The rule’s investigation entries are misconfigured: the block says “The rule’s investigation entries are misconfigured and were not generated”, with Edit rule
- The alert rule has been deleted: “The alert rule was deleted, so no investigation entries were generated”
- The alert came from an older Edge: upgrade to v0.75.3 or later and new alerts will include investigation entries
- The snapshot exceeds 8KB: view the entries in the monitoring alert details
Detail tabs
The incident details page contains 7 tabs; some appear only under certain conditions:Timeline comments
The top of the Timeline tab provides a Markdown comment box that supports:- Writing notes, troubleshooting memos, or meeting summaries in Markdown syntax
- Pasting or uploading images directly; screenshots are auto-uploaded and converted into image links
- Click an image in a comment to preview the original image without leaving the page
- Mention members with @ in a comment to send them a personal notification containing the comment and an incident link. Notifications follow the member’s @mention settings under Personal Center → Notification Preferences, with email, SMS, or IM channels available
- Appending the published comment as a record on the incident timeline, interleaved with system-generated events for easy retrospection
@mention notifications are dedicated personal notifications and are not affected by notification muting such as snooze or silence rules.
Comment types
Comments can carry a comment type tag to distinguish their nature on the timeline (for example, “root cause analysis” or “handling progress”):- When posting a comment, pick a type, or No comment type, in the Comment type selector next to the comment box. The timeline shows the type as a colored tag
- Comment types are configured at the account level and apply to all incidents under the current account; renaming or recoloring a type also affects historical comments
- The selector next to the comment box only appears when the account already has comment types, or when you have comment-type management permission
The limits above apply to the Manage comment types dialog in the console. In the Flashduty App (mobile), types appear as pills above the comment box. With management permission you can create a type from the More panel (name up to 20 characters, one of 30 preset colors, no custom color); rename, recolor, delete, and reorder in the console.
Action item and follow-up events
The timeline records every operation on action items and follow-ups with an icon, alongside comments, acknowledgments, and other events. These operations are create, update, change assignees, complete, delete, convert an action to a follow-up, and link a follow-up to the post-mortem. When the incident closes, one record summarizes the unfinished actions that Flashduty converted. When a create or assignee-change record carries assignees, the sentence continues with “assigned to …”. Members alone appear one by one as avatar plus name. If AI SRE is among the assignees, the record uses a joint signature: member names joined by ”, ”, ending with “and AI SRE” (for example, “John, Jane and AI SRE”).AI SRE action records
AI SRE sometimes acts on behalf of a member, for example when an automation rule writes its conclusion back to the incident. The timeline signs these actions{{name}} and AI SRE, because AI SRE uses that member’s identity and permissions.
Each such row has a Continue conversation entry that opens the original session in the AI SRE panel (one incident can have several sessions). This requires AI SRE to be enabled for the account and permission to use AI SRE chat; personal sessions (visible only to their creator) and expired sessions cannot be continued.
Change history
The Change History tab shows change events close in time to the incident, so you can see whether a recent deployment or configuration change caused it. The change event list displays the following information:
You can adjust the query scope through the filter at the top, including time range and change source. Expand any row to view a timeline visualization of that change event, allowing comparison with the incident trigger time.
Post-mortem
The incident details page has a built-in post-mortem editor, and a shortcut button in the action area jumps straight to the Post-Mortem tab. There you can create a post-mortem, AI-generate a first draft, edit the title and rich-text content, publish, re-edit after publishing, delete, and export as Markdown. See Post-Mortem for details.War room operations
When an incident has a war room, the More menu offers Invite Followers to War Room and Close War Room. For when these appear, what happens if the IM integration is disabled, and the mobile app, see War Room.FAQ
Console error: Due to the large volume of data, we are unable to respond...
Console error: Due to the large volume of data, we are unable to respond...
This error often appears on incident/alert list queries, analytics dashboards, and so on. It’s mainly because the system matched too much data and the query timed out.In this case, narrow your query scope, such as time range, or use more precise query conditions. If issues persist, contact us.