

Third-party app integration
Install the Flashduty app in WeCom
If your enterprise has never installed the Flashduty app, install it in the admin console first; skip this section if it is already installed.-
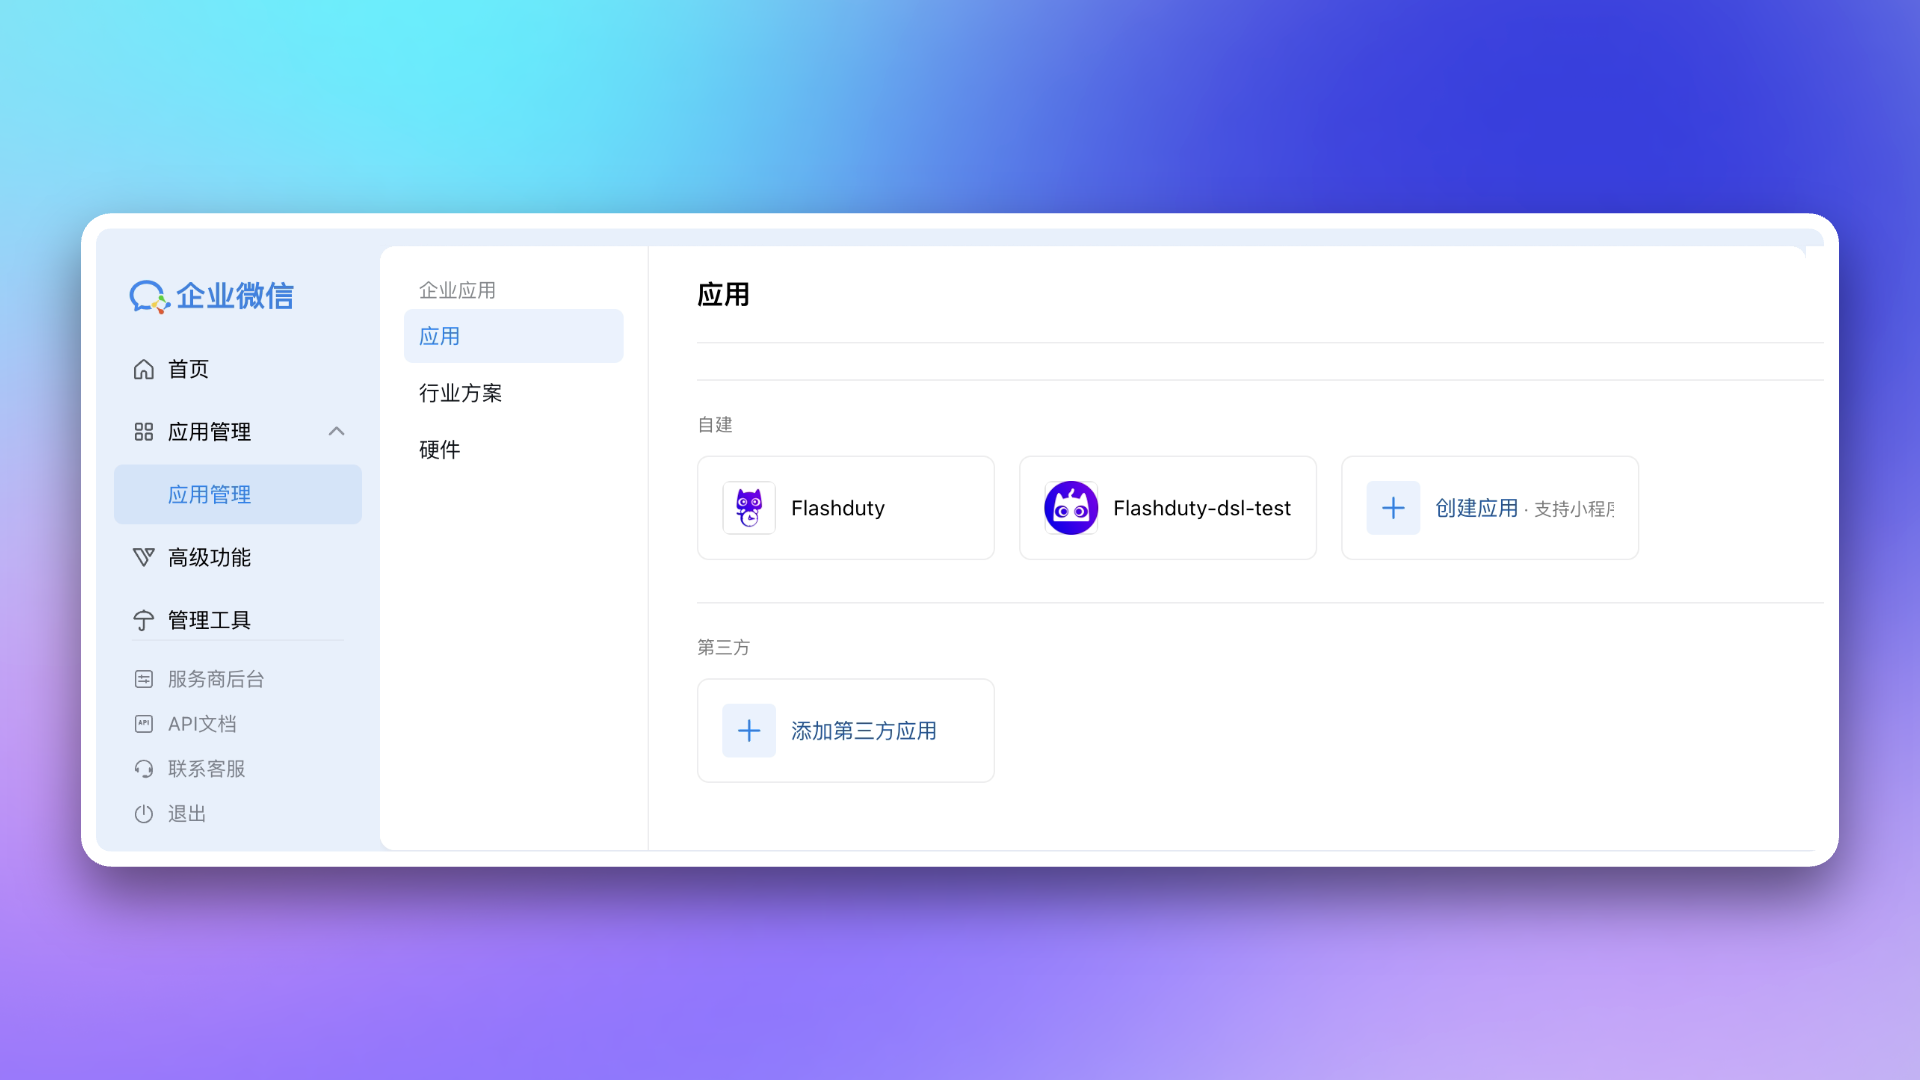
Visit WeCom Admin Console, go to App Management → Apps page, click Add Third-Party App.
-
Enter
Flashdutyin the search bar, after finding the app, click Add.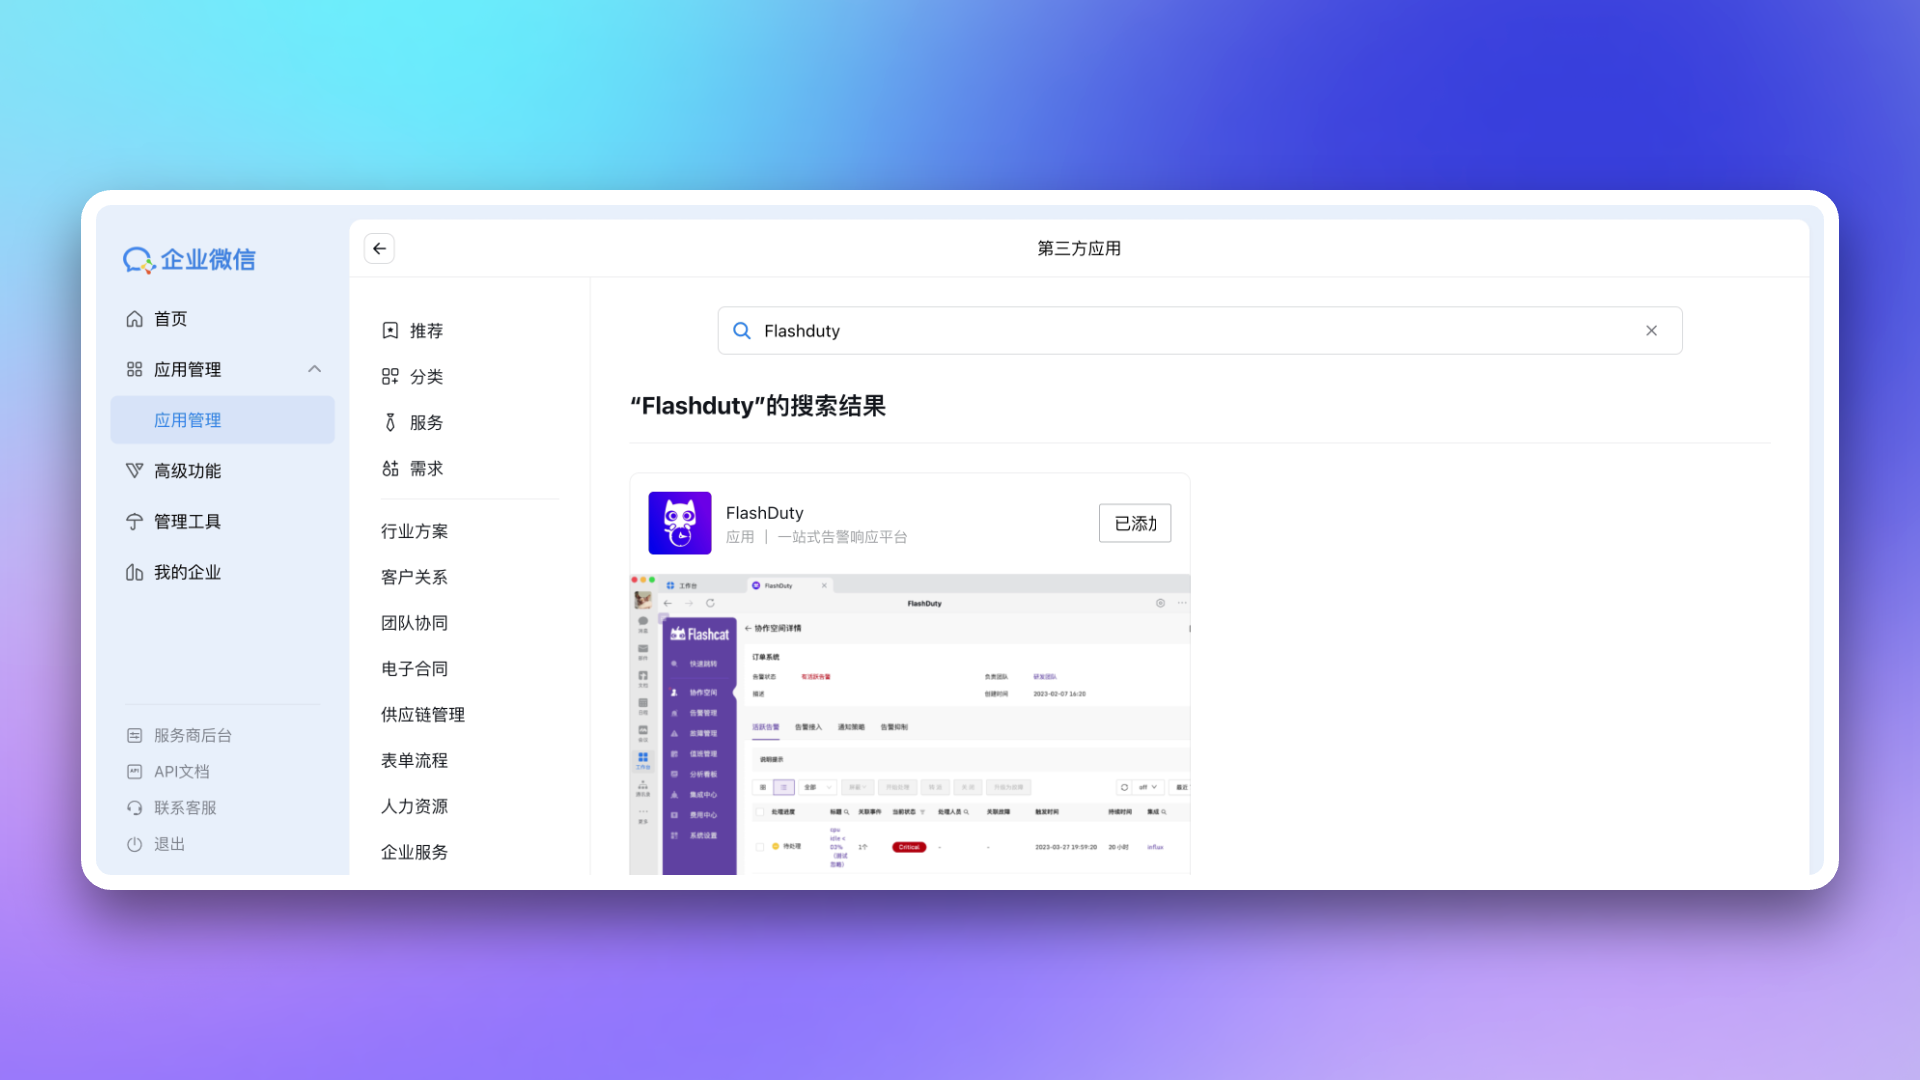
-
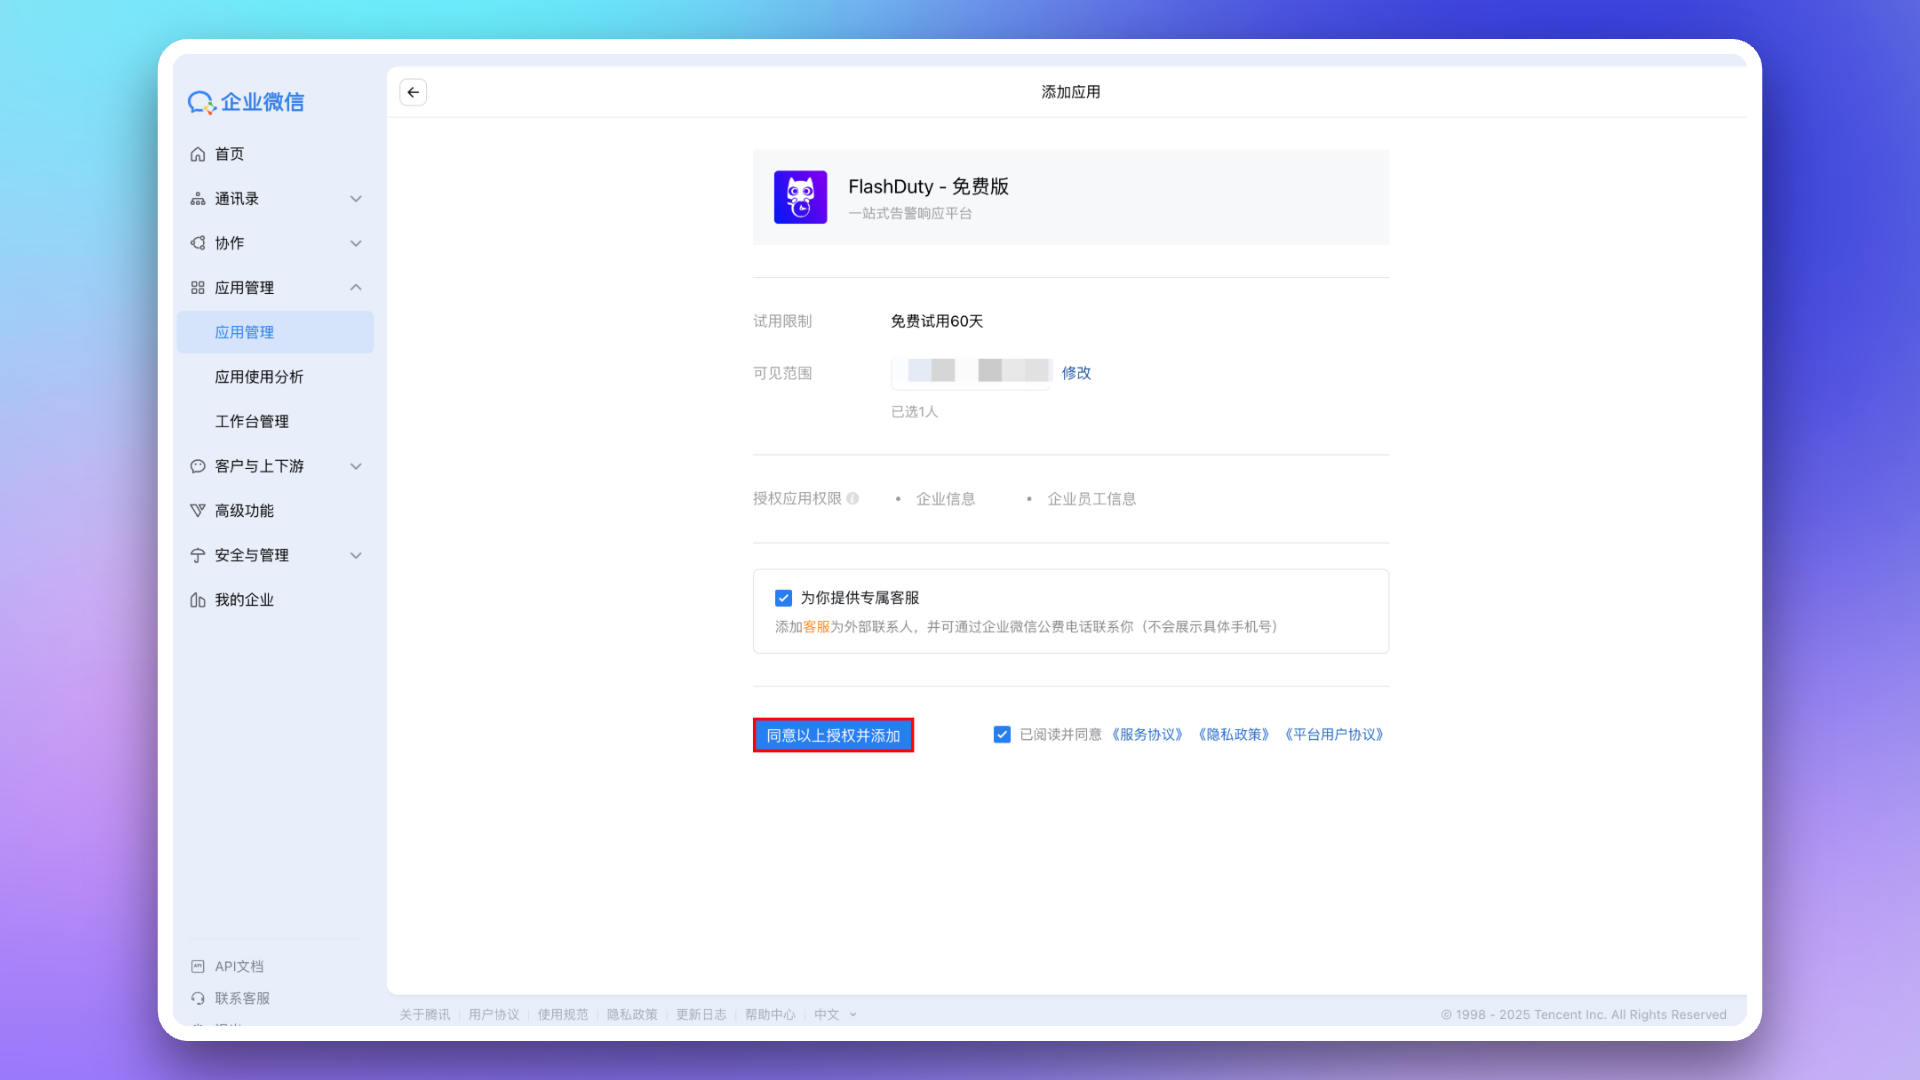
Modify app Visibility, recommend selecting all employees or specific department nodes to avoid modifying when new enterprise members join. Then click Agree to the above authorization and add to complete installation.
Bind the enterprise by QR code in Flashduty
Create the WeCom integration
Choose how to bind the enterprise
Scan and confirm the binding in WeCom
- For “not installed yet”, click Open the WeCom authorization page and complete the authorized install as a WeCom admin. If you are not the admin, send the link in the dialog to your admin; the dialog continues automatically once the admin finishes.
- For “already installed”, scan the QR code with the WeCom app, or send the link to any member of that enterprise to open in WeCom.
- Enterprise ID becomes read-only and shows “Confirmed through WeCom and cannot be changed.”. Switching enterprises requires scanning again; there is no field to edit the ID directly.
- A bind session is valid for 30 minutes and can be used once. After it expires the dialog says “The link has expired. Generate a new one.” — click Generate again and scan again.
- When binding fails the dialog explains why:
This enterprise has not installed the Flashduty app. Close this dialog, choose "Flashduty app not installed yet", and install it first.(the enterprise has no app but “already installed” was chosen),The binding was cancelled on the WeCom page.(Cancel was clicked on the confirmation page),WeCom did not complete the confirmation. Generate a new link and try again.(anything else).
Custom app integration
War Room and @ AI SRE in group chats work only in this mode, which is also the default Application version when you create a WeCom integration.Create the integration and fill in the credentials
Create the app in the WeCom admin console
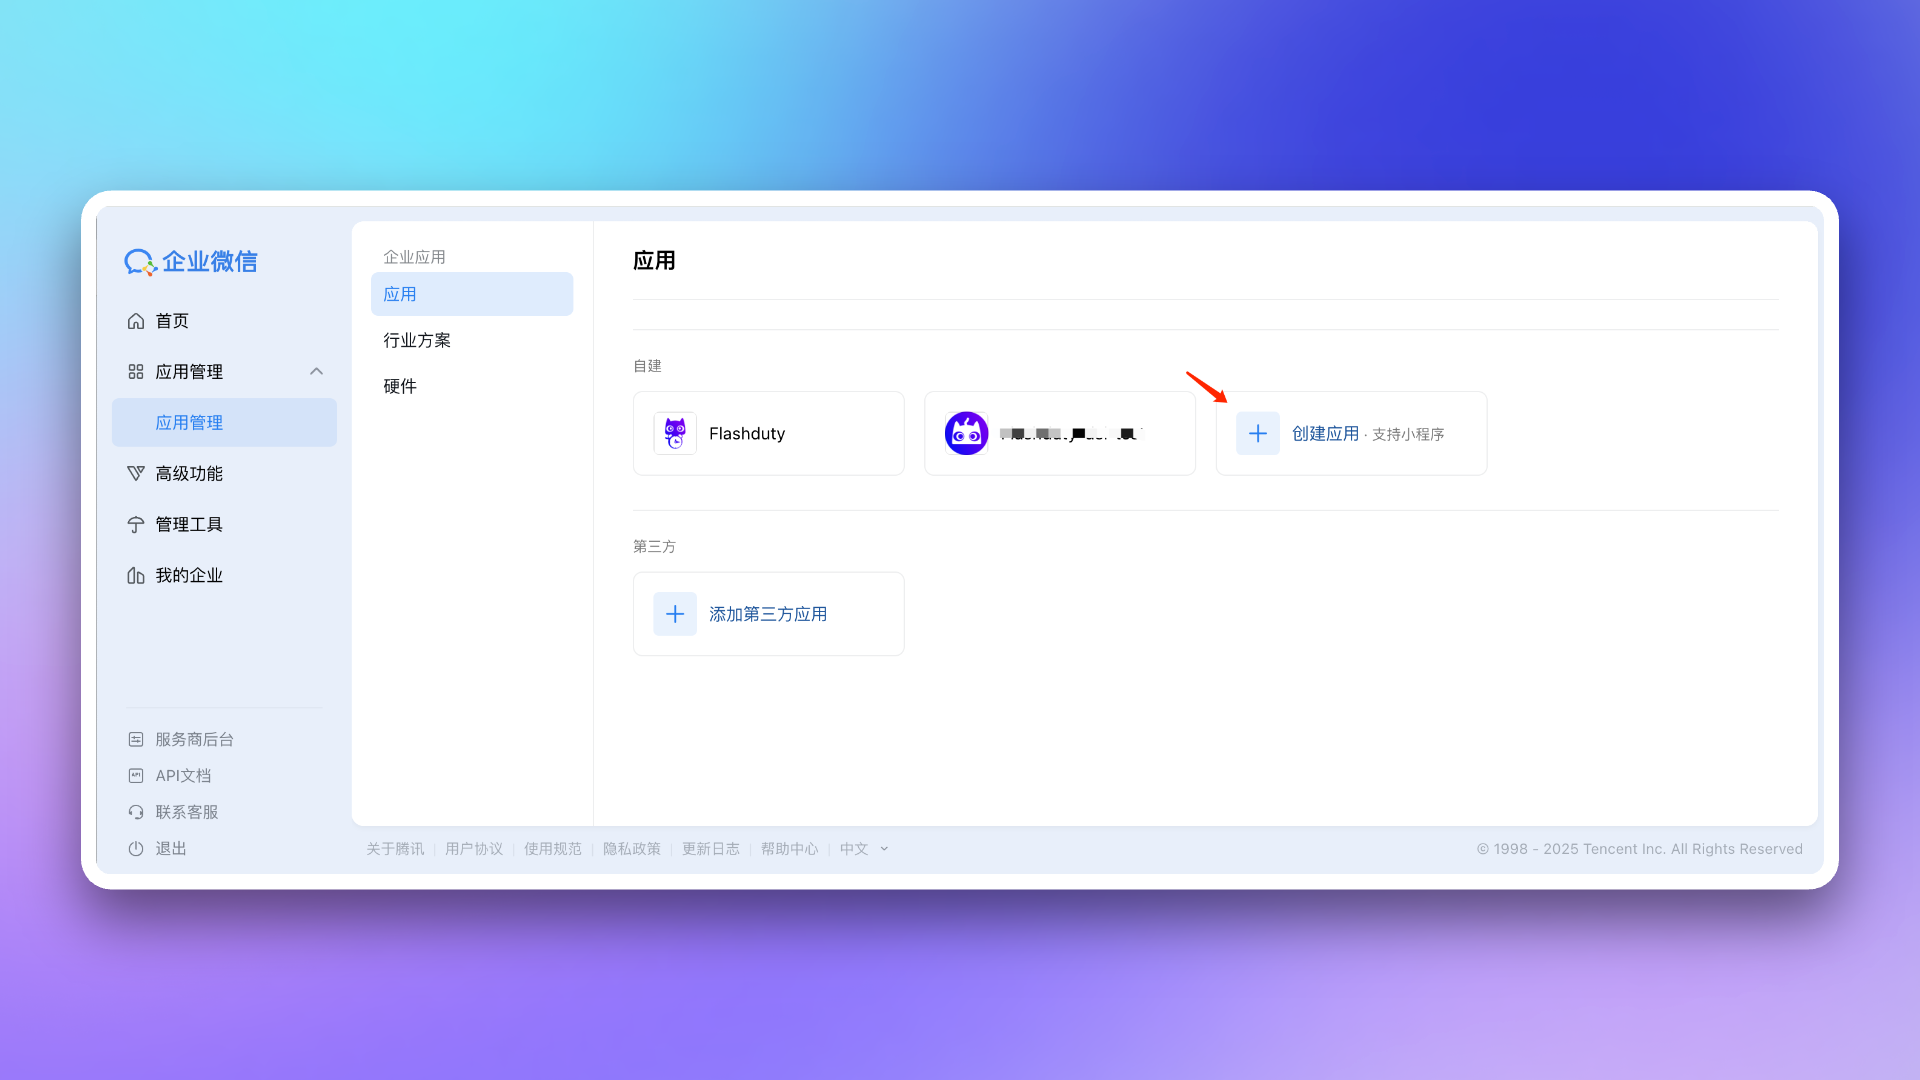 Configure App Logo, App Name, and App Visibility.
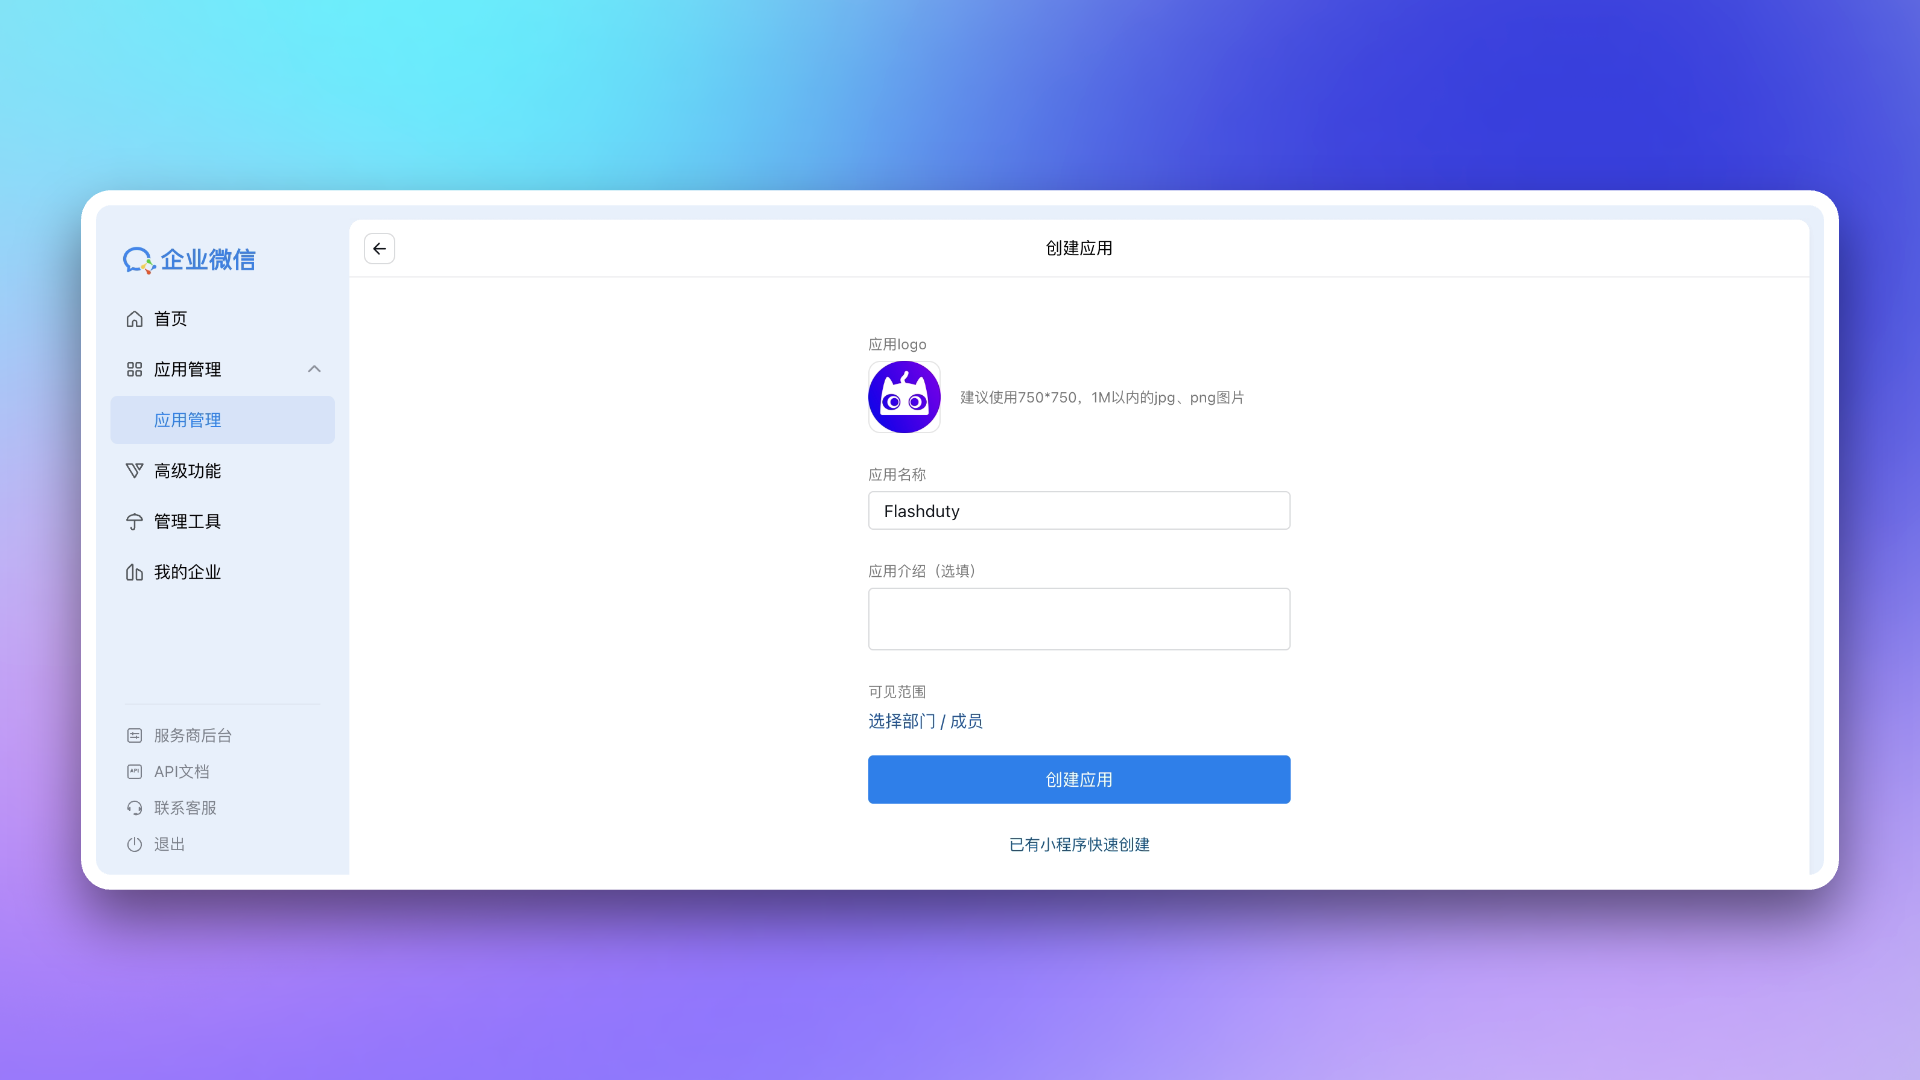
Fill in the enterprise ID, AgentId and Secret
Enterprise ID from the My Enterprise page and AgentId and Secret from the App Details page of the app you just created, then fill them in the Flashduty On-call integration configuration page.If your WeCom is a private deployment, also fill in Endpoint. The Flashduty service must be able to reach that Endpoint; you can set up whitelist authorization for it.Fill in the access domain
https://, no path, and no port when Flashduty hosts it, for example flashduty.example.com.After you save, connect this domain in step 1 of the detail page: add CNAME records so Flashduty issues the certificate and forwards traffic, or forward it with your own Nginx. WeCom requires the trusted domain and the callback URL to use this domain.Save the integration
Token and EncodingAESKey for receive messages and for the smart robot are all generated by Flashduty; you do not fill them in when creating the integration, you generate them in the matching step on the detail page.After saving, the Finish setup in WeCom section on the detail page walks you through the rest.Finish setup in WeCom
The detail page lists six steps in this order, numbered the same as this section. Steps whose outcome WeCom reports are ticked automatically; for the steps nothing reports back, click the confirm button inside the step once you have done it, which requires permission to edit the integration.1. Connect the access domain
There are two ways to connect the access domain; pick one:- CNAME hosting (recommended): add CNAME records at your DNS provider. Flashduty issues the certificate and forwards traffic, so there is no server for you to maintain.
- Forward it yourself: set up the certificate on your own Nginx or load balancer and forward every request for this domain to Flashduty. This is the only option when the domain is in use elsewhere and cannot be hosted.
CNAME hosting
Add the CNAME records shown in step 1 of the detail page at the DNS provider that hosts the access domain:wecom.flashduty.com (Hong Kong) is the default and works for any domain; if the domain has completed ICP access filing on Alibaba Cloud, you can use the mainland entry cn.wecom.flashduty.com instead for faster access inside China; if your DNS provider supports region-based resolution, configure both. A domain without Alibaba Cloud ICP access filing that points at the mainland entry is blocked by Alibaba Cloud.
Once the records resolve and the certificate is issued, step 1 is ticked automatically and shows “Resolving · Certificate issued”. While records are missing it shows “N record(s) not resolving yet”; when every record resolves but the certificate is still being issued it shows “Issuing certificate”. Click Check again to read the state again.
Forward it yourself
Requirements for forwarding it yourself:- A certificate issued by a trusted CA.
- Every path of this domain forwarded to
wecom.flashduty.com, with the originalHostheader kept. Flashduty identifies the integration byHost; when Flashduty adds or changes paths later, your config stays the same. - Both http and https forwarded, with no redirect: WeCom fetches the domain verification file over http.
- If the domain has completed ICP access filing on Alibaba Cloud, you can forward to
cn.wecom.flashduty.cominstead for faster access inside China.
https://<access domain>/ping answers pong, step 1 shows “Self-hosted proxy · Reachable”.
2. Set the trusted domain
On the app details page, go to Developer Interface → Web Authorization & JS-SDK, click Set Trusted Domain, and enter the access domain. See WeCom’s Enterprise Internal Development Domain Configuration Guide for the requirements.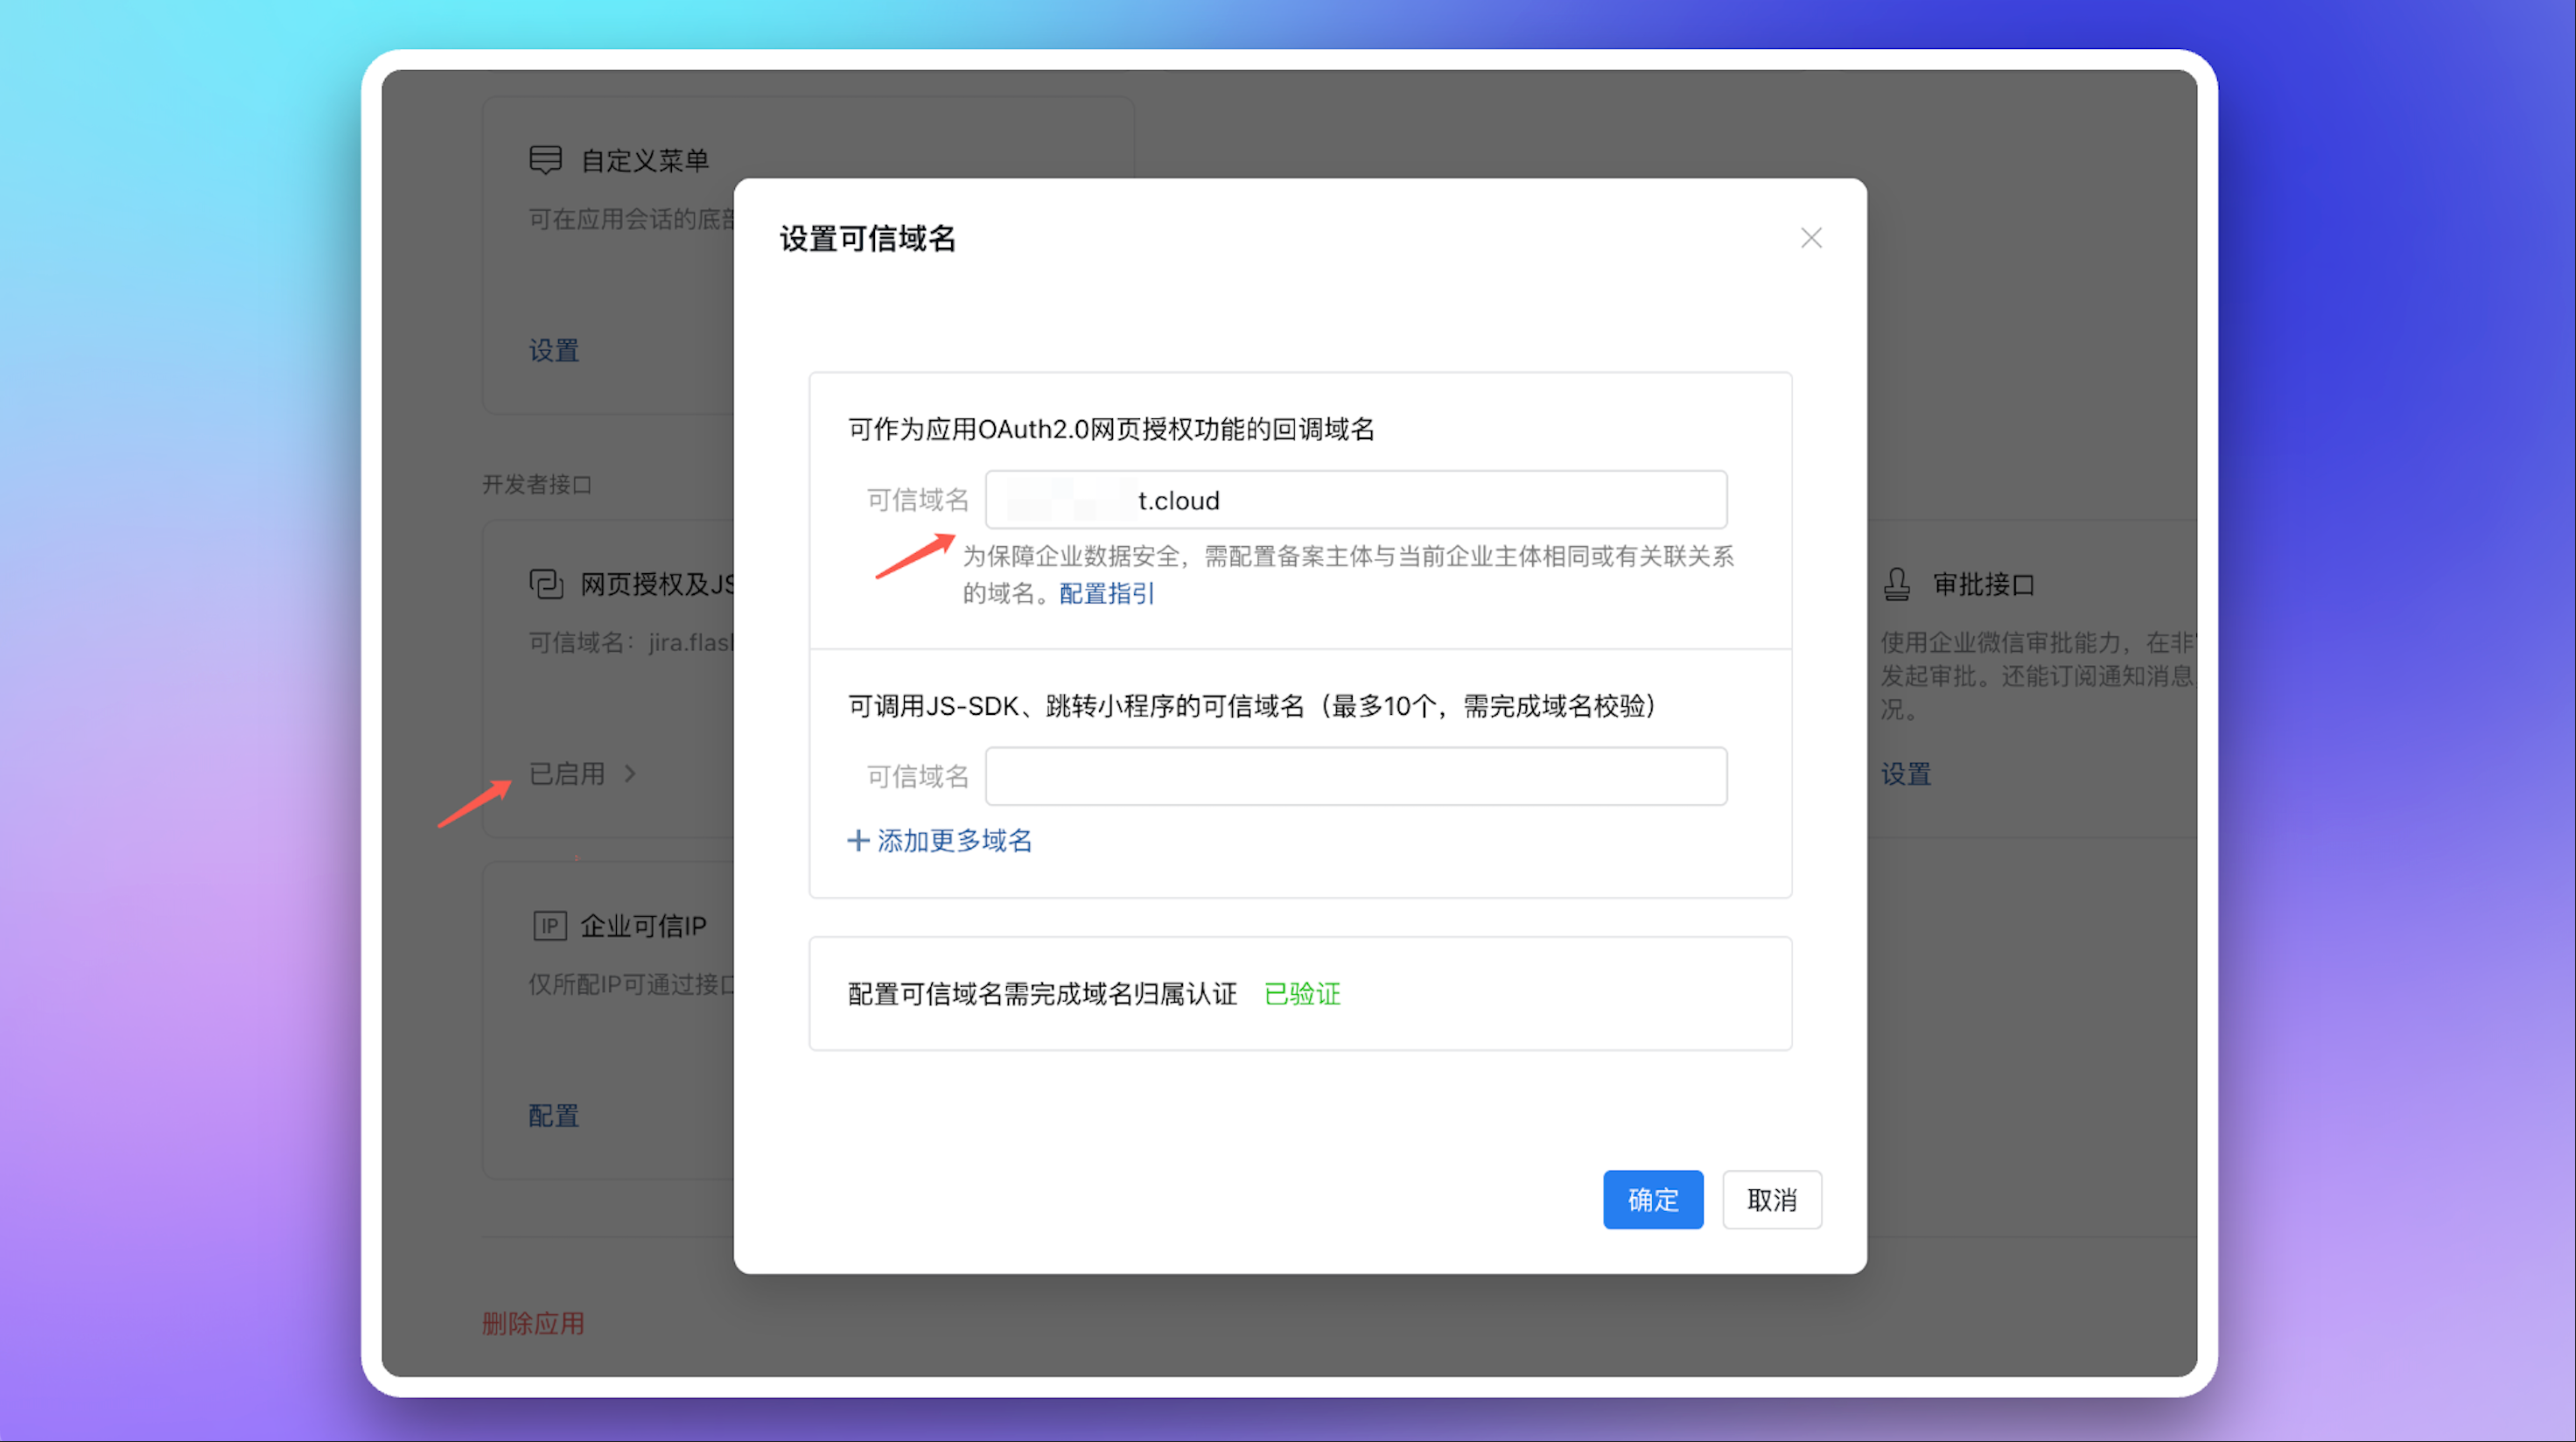 Then on that page click Request domain verification, download
WW_verify_xxx.txt, and back in step 2 of the detail page click Upload verification file to upload it. WeCom fetches this file from the document root of the domain, and Flashduty serves it there (WeCom follows no redirect, so both http and https must serve it directly).
Once WeCom has fetched it, step 2 is ticked automatically and shows “WeCom fetched the verification file”; while waiting for WeCom to fetch an uploaded file it shows “Waiting for WeCom to fetch it”, and before uploading it shows “Verification file not uploaded”.
Back in WeCom, click OK to finish the verification. Fill the same domain into the OAuth2.0 web authorization callback domain on the same page.
/WW_verify_*.txt to Flashduty, so upload the file on the detail page as usual. For a private deployment, or if you serve the verification file from the document root of your own server instead, both http and https must serve it directly, with no redirect; once verification passes, click I’ve verified it to record the step.3. Set up API message receiving
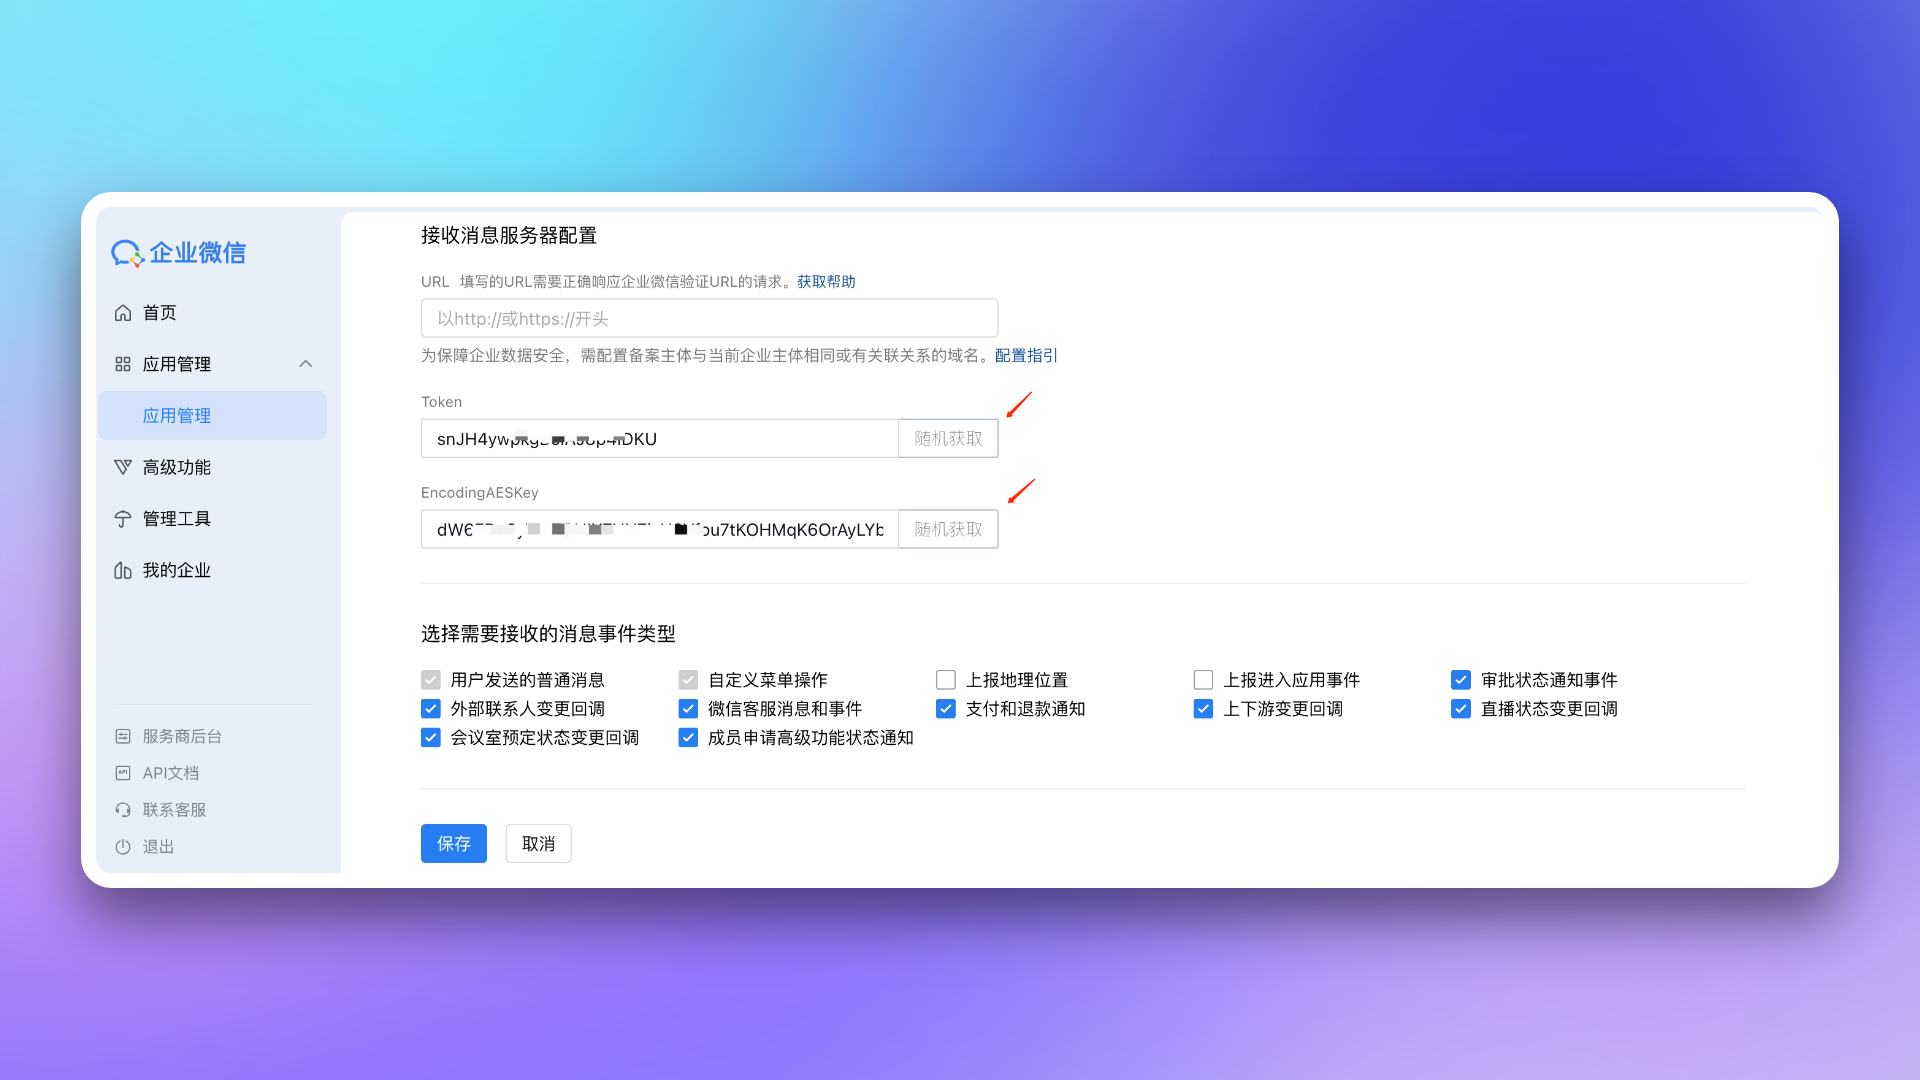
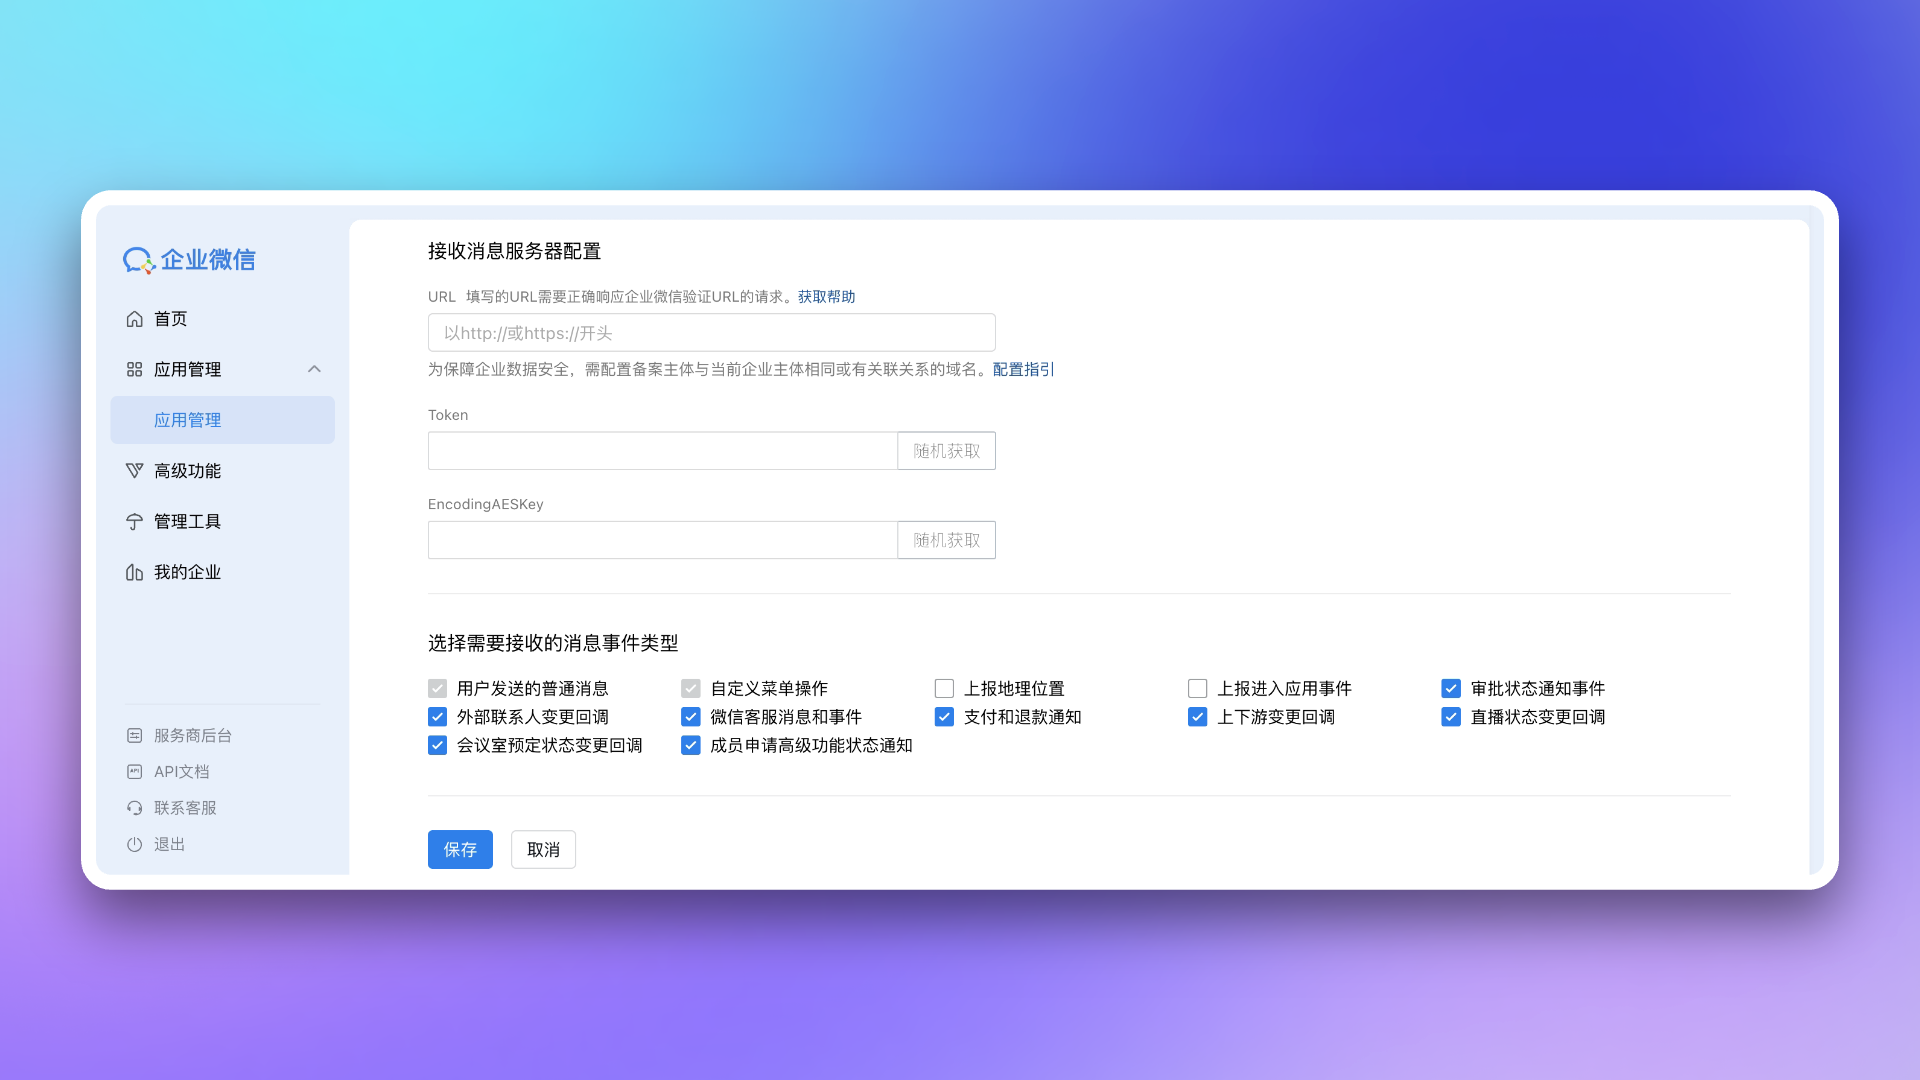
On the app details page, go to Receive Messages → Set API Receive, fill in the three items shown in step 3 of the detail page, and click Save:Token and EncodingAESKey are shown only once and only a masked value remains after you leave the page, so copy them into WeCom right away. To replace them, click Generate again: the pair already saved stops working immediately, so any old value still in WeCom must be replaced and saved, otherwise callbacks stop arriving; it goes back to “Waiting for WeCom to verify” and is ticked again only after WeCom verifies the new pair.
4. Configure the trusted enterprise IP
At the bottom of the app details page, click Trusted Enterprise IP to configure it, then copy the whole IP line shown in step 4 of the detail page into it. On SaaS the line is47.93.12.134;47.94.95.118;123.56.8.183;47.94.193.81;1.13.19.96, and every enterprise using Flashduty enters this same line; for a private deployment, enter the egress IP your Flashduty servers use to reach WeCom.
WeCom only allows configuring the trusted IP after step 2 or step 3 is done.
Step 4 is determined by Flashduty running one check against WeCom: a successful check shows “Active”; WeCom answering 60020 shows “Not set up”, meaning the trusted IP is still missing; any other error code is shown as WeCom returned it; an unreachable WeCom shows “Check failed”. Click Check again to read the state again.
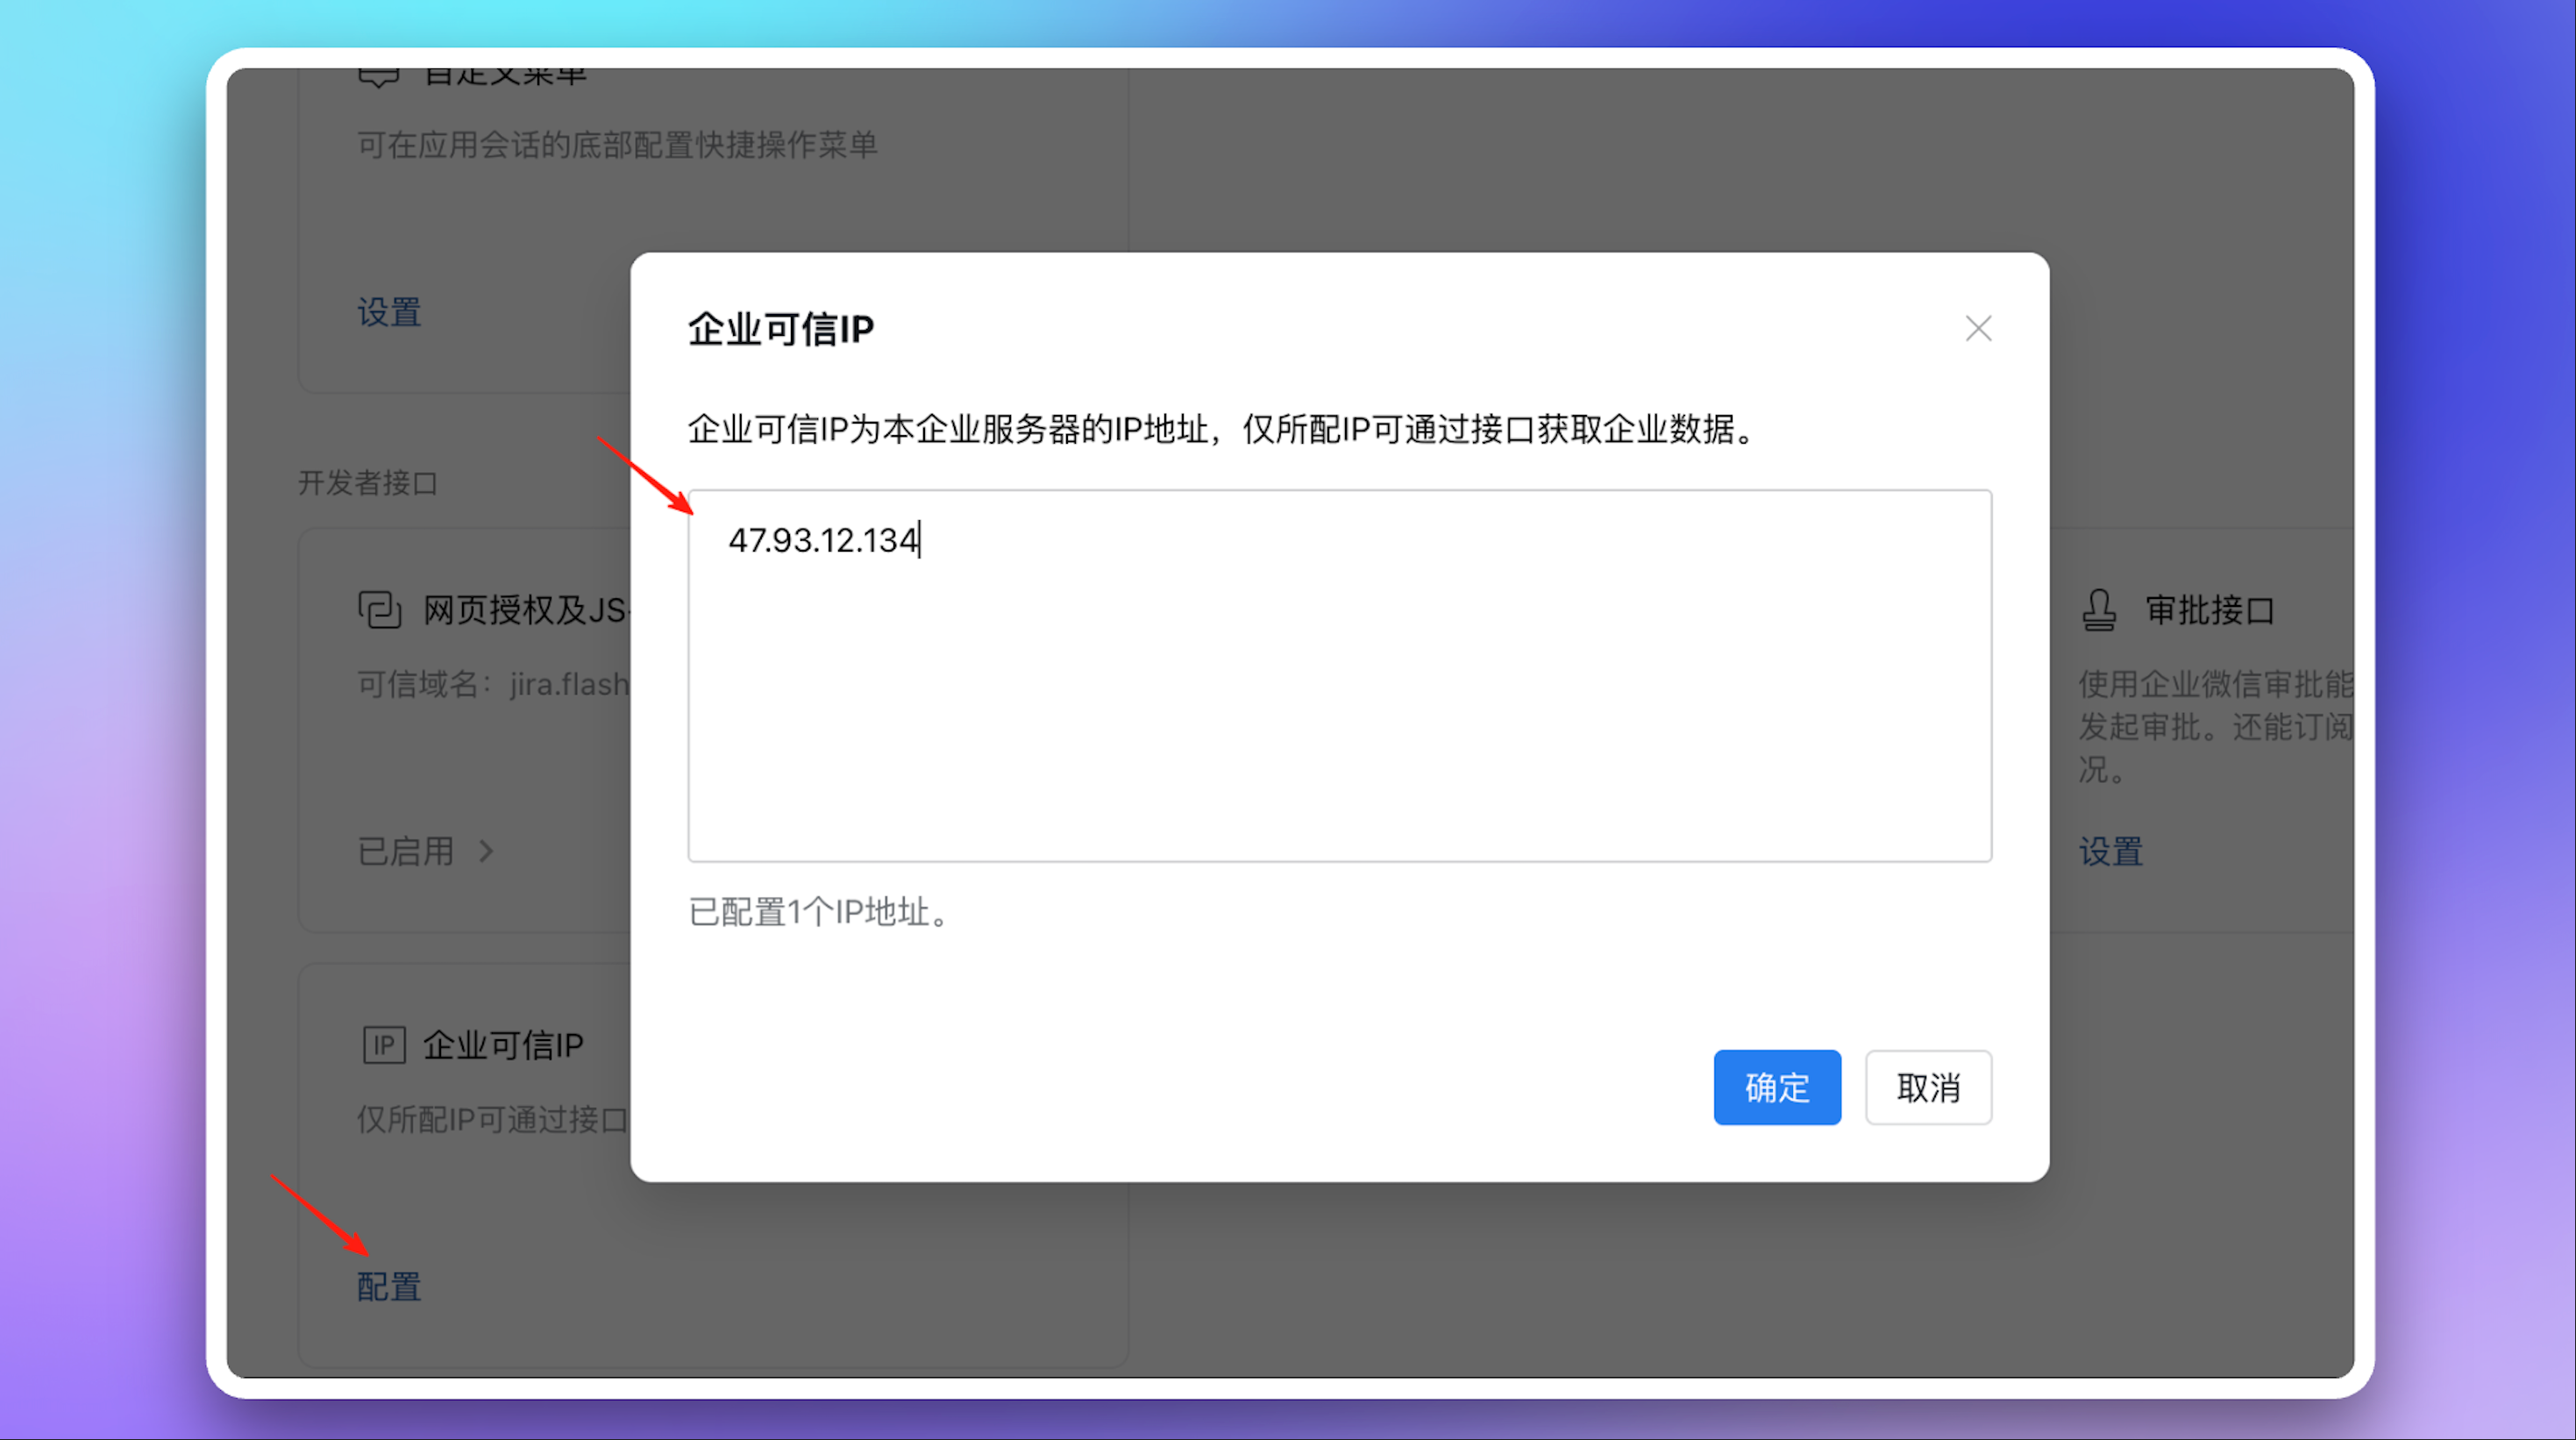
Endpoint is set (that is, while Flashduty proxies the WeCom calls). If WeCom reports “the following IP belongs to a third-party service provider”, send a screenshot to Flashduty support. For a private deployment, enter the egress IP of your own Flashduty server.5. Set the workspace app homepage
On the app details page, click set on Workspace App Homepage, choose Web page, and enter the address shown in step 5 of the detail page. A newly created integration has no separate “frontend trusted domain” to configure. WeCom does not report this setting back, so click I’ve set it after configuring it.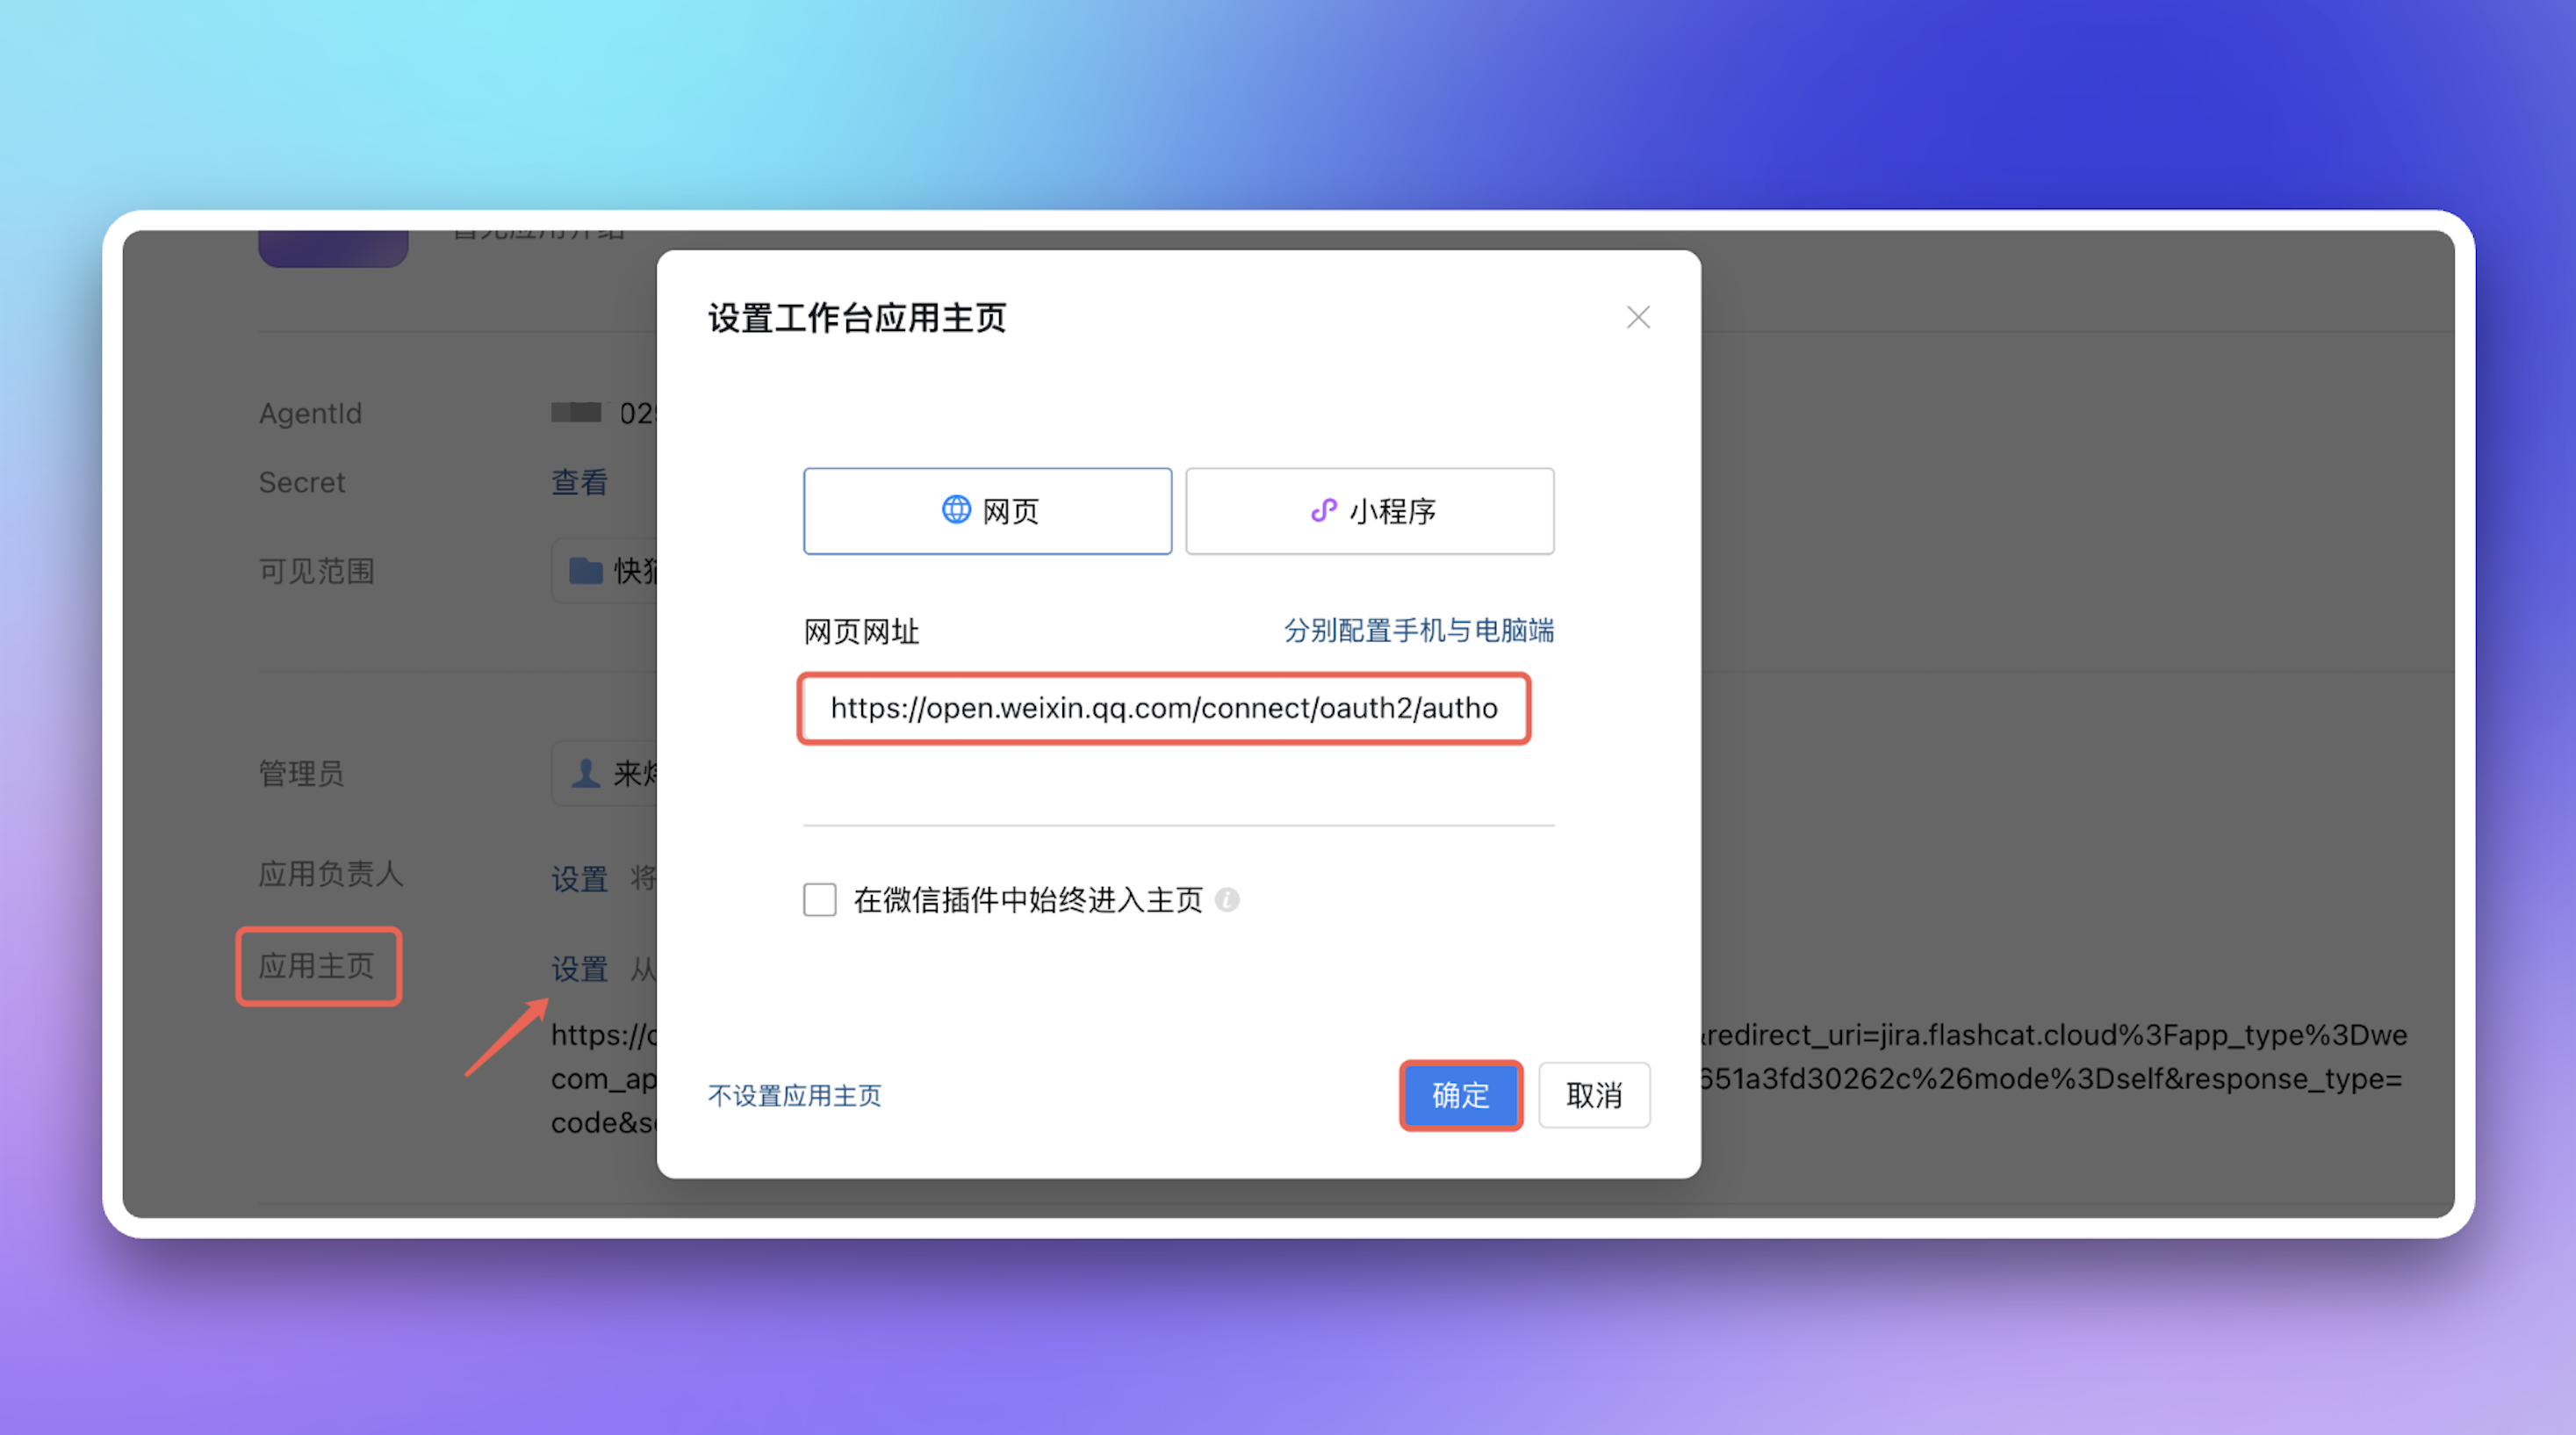
6. Create the smart robot (optional)
An optional step for @mentioning the smart robot in single chats and group chats to use AI SRE; see Configure the AI SRE smart robot for the details. Step 6 giveshttps://<access domain>/event/push/wecom/bot?integration_key=<integration_key>, and its Token and EncodingAESKey are likewise generated by Flashduty, shown once, and not interchangeable with the receive-message pair. The step is ticked automatically once WeCom verifies the URL.
Linked users
In the Linked Users tab of the integration detail page, filter members by All / Linked / Unlinked, or search by name or email. Click One-Click Link to match members to WeCom accounts by their phone number or email and link them automatically, the same result as a member logging into Flashduty from WeCom. Members receive WeCom notifications only after they are linked. If linking fails, verify that the member’s phone number or email matches their WeCom account.Configure war room
After completing previous steps, in the Flashduty On-call integration configuration page’s Enhanced Features section, check Enable War Room to activate this feature—no additional configuration needed. Only one IM integration can have War Room enabled at a time; turn it off in the other integration first. See War Room.AI SRE controls
Configure the AI SRE switch under Enhanced Features. It is enabled by default; see IM platform for what it does. The two WeCom app modes support different AI SRE entry points:Configure the AI SRE smart robot
@mention the Smart Robot in a WeCom single chat or group chat to start an AI SRE investigation session without leaving WeCom. The Smart Robot can only be configured in Custom App Integration mode.- AI SRE must be enabled for your account, and Allow AI SRE conversations in IM must be on in the Flashduty WeCom integration (War Room is not required). Otherwise the robot does not respond to messages.
- The callback URL is built from the Access Domain saved in the integration, so save the integration and its access domain first as described in Custom App Integration; only then does step 6 of the detail page show a usable URL.
Create a Smart Robot in WeCom
Enter the callback URL
URL shown in step 6 of the Flashduty WeCom integration detail page. Its format is:Generate the Token and Encoding-AESKey
Token and EncodingAESKey, and enter both values together with the URL above on the Smart Robot’s API configuration page, then save.Do not click “Random generate” in WeCom: both sides must use the same pair Flashduty generated.The plaintext is shown only at generation time; afterwards only a masked value remains. Clicking Generate again makes the previous pair stop working immediately: replace the old values in WeCom, save, and verify the callback URL again (the step is ticked again only after that verification passes).How to use
Once configured, @mention the Smart Robot in a WeCom single chat or group chat and type a question or incident description to start an AI SRE session. Supported message types:FAQ
The robot receives messages but returns no response
The robot receives messages but returns no response
- Confirm that AI SRE is enabled for your account and Allow AI SRE conversations in IM is on in the integration.
- Confirm the
integration_keyin the callback URL exactly matches the value shown on the Flashduty integration details page. - Confirm the
TokenandEncoding-AESKeyentered in WeCom are the pair generated in step 6 of the detail page (Smart Robot), not the pair generated in step 3 (Receive Messages). - Check the robot’s callback records in WeCom (if available) to see whether requests arrive and whether any error codes are returned.
'URL verification failed' when saving the callback URL
'URL verification failed' when saving the callback URL
- Confirm that the Flashduty server is publicly reachable by WeCom servers and that the access domain is reachable: with hosting, the DNS records from step 1 must resolve and the certificate must be issued; when you forward it yourself,
https://<access domain>/pingmust answerpong. - Confirm that the
TokenandEncoding-AESKeyentered in WeCom exactly match the pair generated in step 6 of the detail page. - Confirm that the
integration_keyparameter in the callback URL is correct and that the corresponding integration is enabled.
Signature verification failure (invalid signature)
Signature verification failure (invalid signature)
Token or Encoding-AESKey is wrong. The Smart Robot’s credentials and the custom app’s Receive Messages credentials are two independent sets. Generate the matching set again in step 6 (Smart Robot) or step 3 (Receive Messages) of the detail page, enter the new values in WeCom and save, then verify the callback URL again.How to complete account linking or message delivery shows 'App not linked'?
How to complete account linking or message delivery shows 'App not linked'?
- Login to WeCom client (desktop or mobile), go to Workspace, find and open the Flashduty app
- First entry requires login. Select your member account, after successful login with a password or SSO, Flashduty account and WeCom account will be linked
- Subsequent app access will be automatically passwordless
How to send incident notifications?
How to send incident notifications?
- Before sending notifications, account linking must be completed as described in the previous question
- Go to the specified channel, navigate to
Escalation Rules→ Personal Channel, selectWeComas notification method - Flashduty On-call supports customizing WeCom notification content. Go to Template Management page to set custom templates
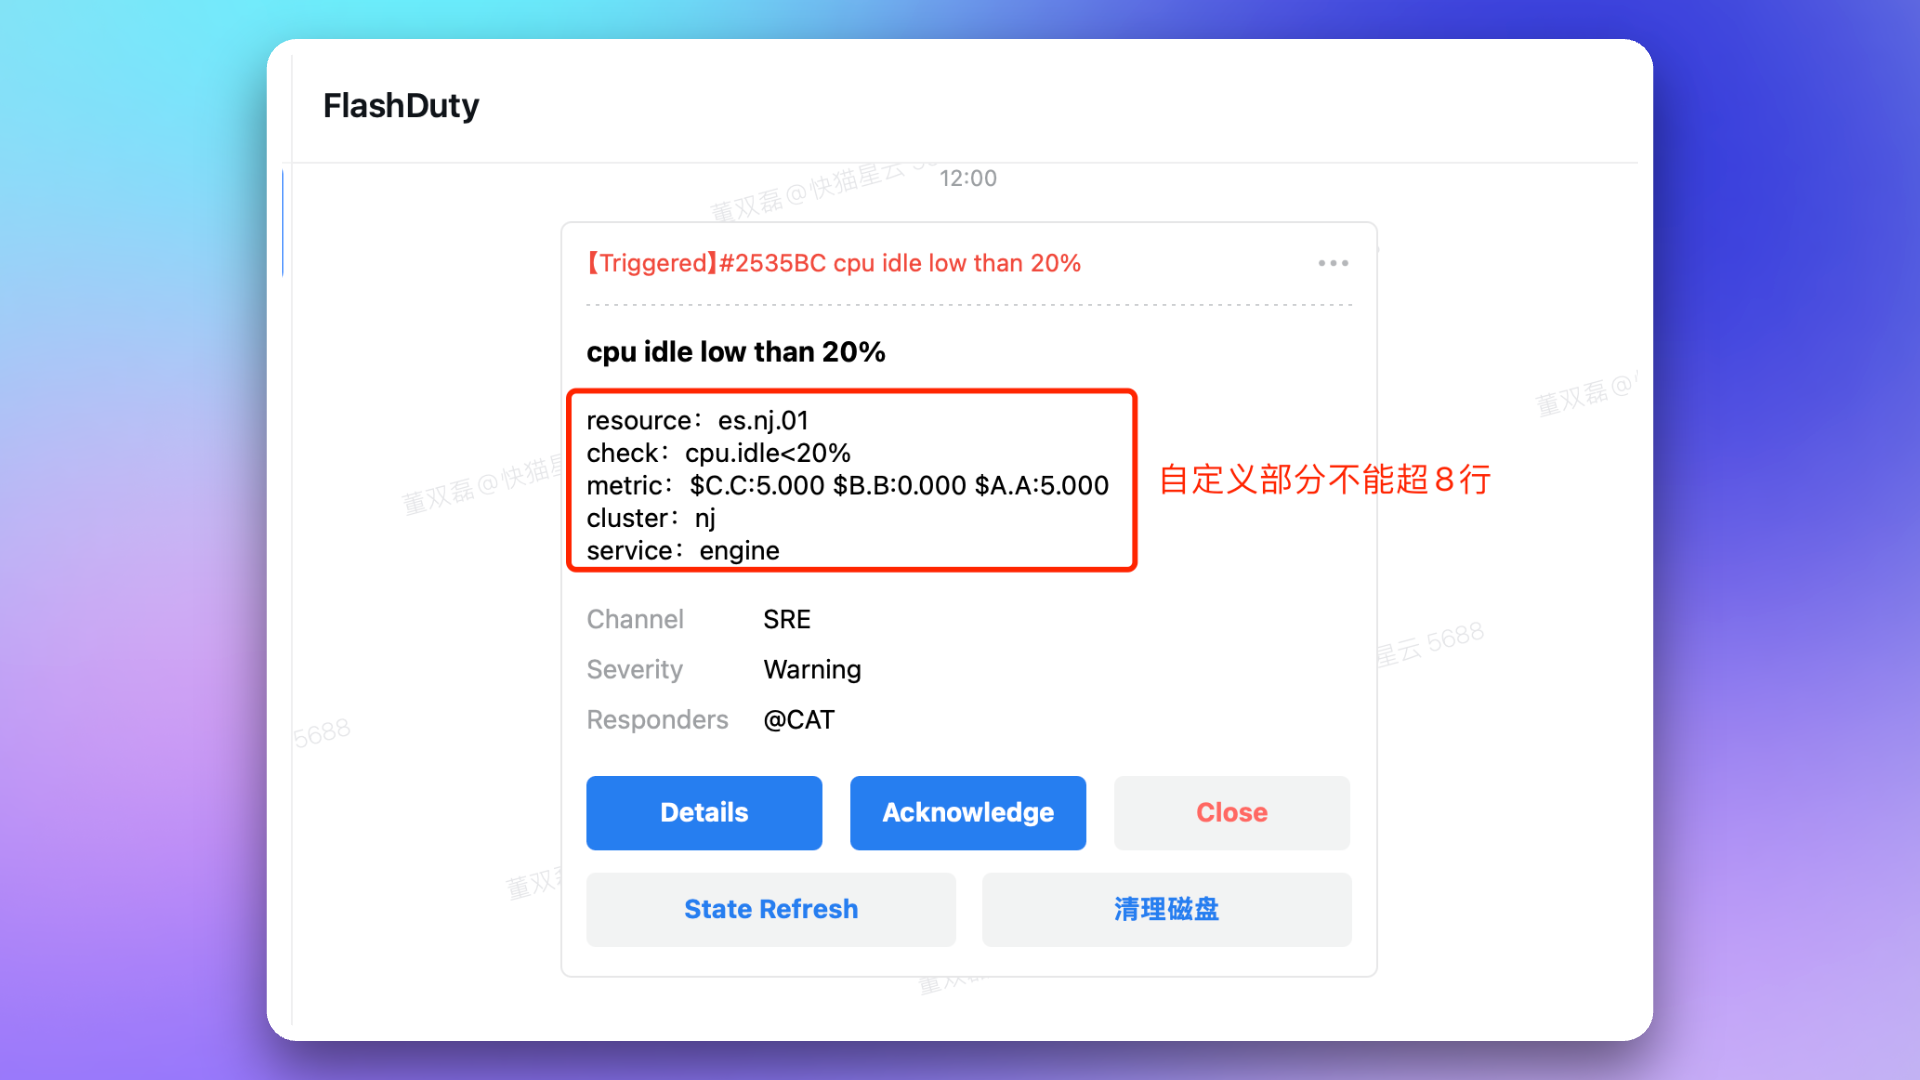
How to handle alerts within WeCom?
How to handle alerts within WeCom?
- Click card message to go directly to alert details page
- Click Start Processing to directly set alert to
Processingstatus - Click Close Directly to directly set alert to
Closedstatus - Click Snooze 2 hours to snooze the alert for 2 hours. For longer snooze times, click
...in the card’s top-right corner for more snooze options
Incident notification failed with 'WeCom license not enabled' prompt?
Incident notification failed with 'WeCom license not enabled' prompt?
Why isn't War Room working as expected?
Why isn't War Room working as expected?
Why does opening the app in WeCom Workspace show 'redirect_uri needs to use app trusted domain'?
Why does opening the app in WeCom Workspace show 'redirect_uri needs to use app trusted domain'?
redirect_uri parameter of the App Homepage URL has completed WeCom’s required domain ownership verification. See WeCom official documentation Enterprise Internal Development Domain Configuration Guide.How to set Mac desktop to open with system default browser?
How to set Mac desktop to open with system default browser?
ctrl + command + shift + d to enable debug mode, then select Debug → Browser, WebView Related → Open Webpage with System Browser. Press the same shortcut to leave debug mode; the setting stays.